Prot forwarding - Add associated filter rule - missing tagging option.
-
I have pfSense firewall in front of our web farm.
I have a bunch of public IPs that I redirect port 80/443 to an internal reverse proxy farm
with added associated filter rules.
The generated rules are actually ignored and only the firs one will be evaluated, because they are exactly the same.
Now I would like to apply different advanced settings per rule, like setting up max states, etc...
I could do that if I were able to set "tag" to the rdr rule, and use "tagged" on the advanced rule settings, but there is no way to do that anymore, or am I missing something.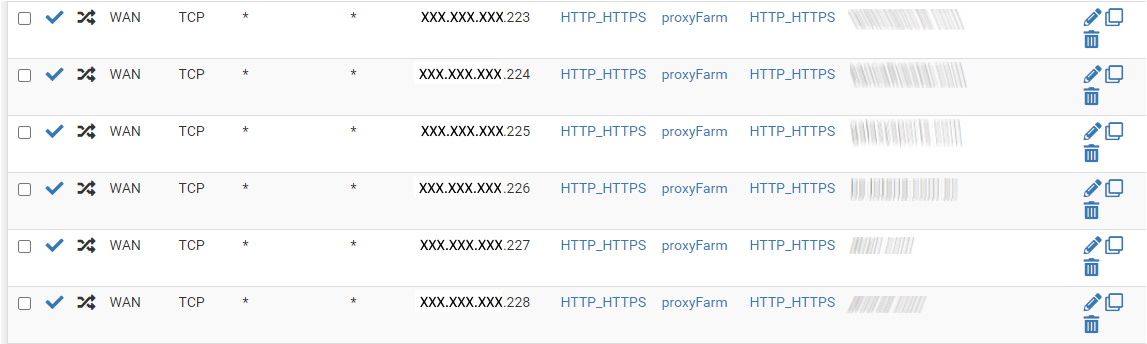
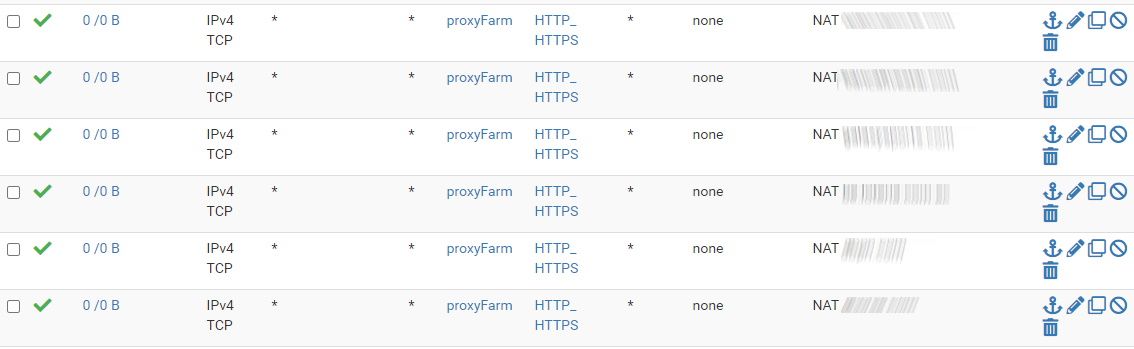
Here are the generated rules:
rules.txt
Copyright 2026 Rubicon Communications LLC (Netgate). All rights reserved.
Privacy Policy · Cookie Policy
Privacy Policy · Cookie Policy