Question about firewall rules and states
-
Hey guys,
I don't really understand the states and the firewall rules.As an example a pass rule for TCP port 80
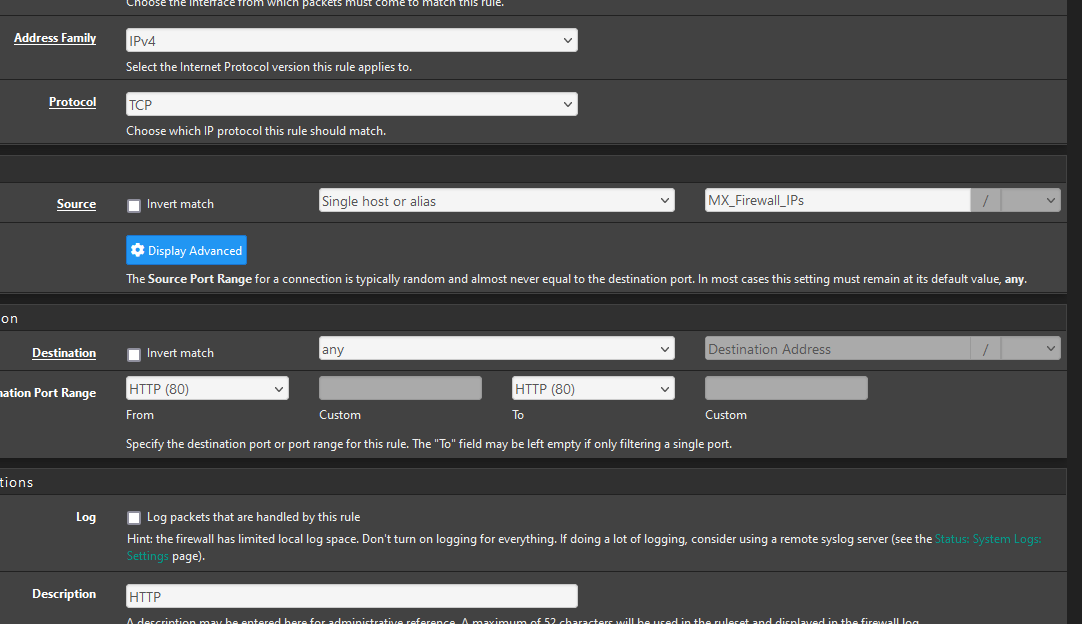
As I understand it, I click on the states in the front to display all connections to TCP port 80.

But there are now also a lot of 443 UDP connections included
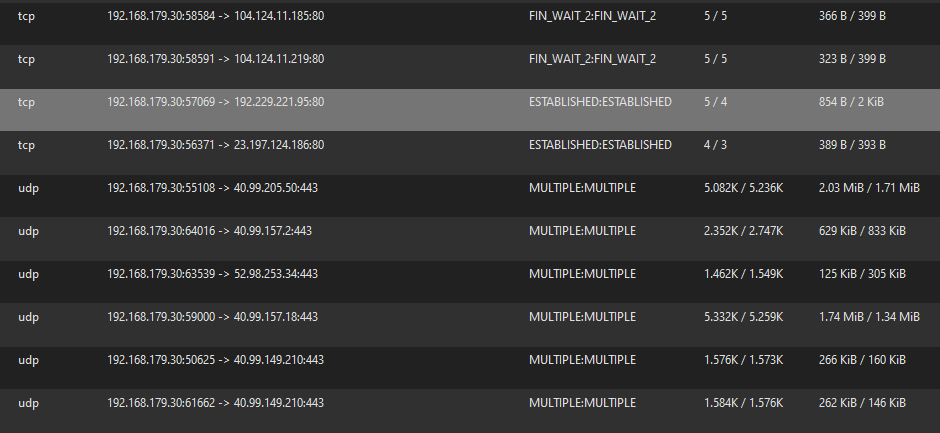
It looks like this for all rules.
Here port 53
There are also a lot of connections to highports in it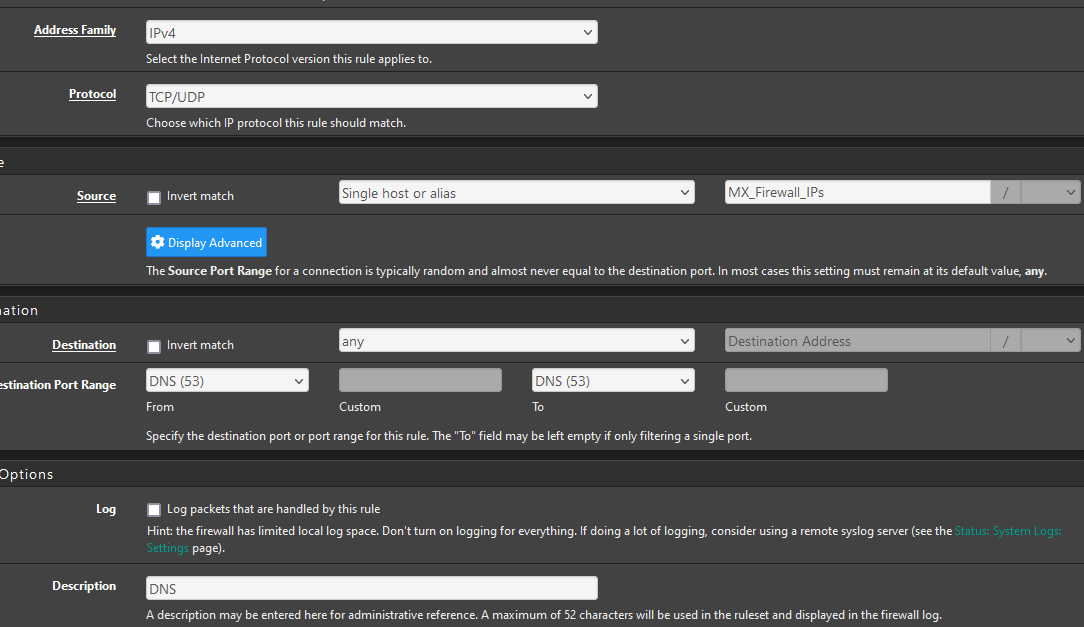
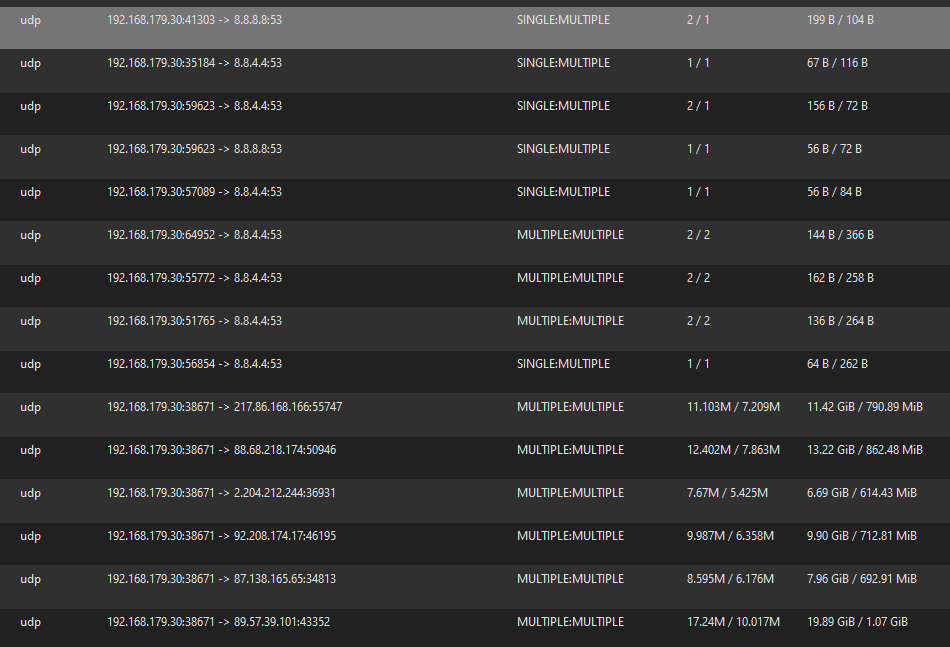
Am I misunderstanding this?
Thank you
Edit:
Where can i find the rule ids?
Can I have them displayed somewhere?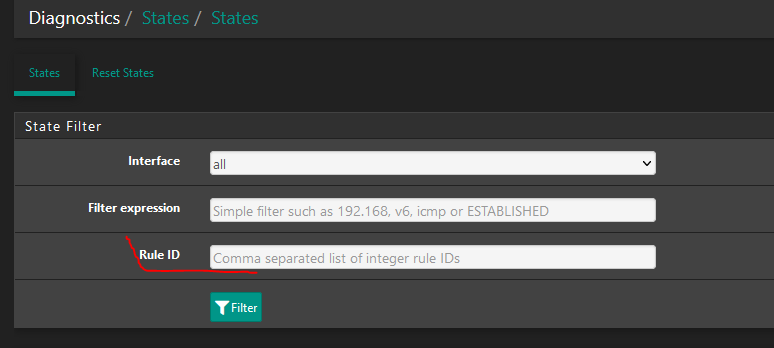
Copyright 2026 Rubicon Communications LLC (Netgate). All rights reserved.
Privacy Policy · Cookie Policy
Privacy Policy · Cookie Policy