This thread is only for the state killing mechanisms as indicated by the title and the initial post in the thread.
If you want to discuss other new options, start a new thread. I have cleaned up the posts in the thread that are not relevant to the new state killing options.
In theory it should work fine, but that large of a jump could be potentially problematic. I can't recall anything specific that might be an issue though. Biggest worry would be something in the upgrade code itself.
Just have a backup and the 2.7 installer image handy and try it when the time comes. Odds are in your favor that it will be fine.
Hmm, it's probably this issue: https://redmine.pfsense.org/issues/13680
Though I don't see any specific errors for each package it is showing the post install script failed. That implies it should have already reinstalled the package but that doesn't appear to be the case.
Steve
There are two threads for this with people contributing in each.
Lets's continue in the other thread: https://forum.netgate.com/topic/180907/pfsense-2-7-0-beta
That particular rule ID is dynamic based on the order pf parses the rules. It could change any time the filter reloads. It's not shown because it's not useful to know on a long term basis.
Yes, it does work pfSense <-> pfSense and also with TNSR (TNSR <-> TNSR and TNSR <-> pfSense).
It may not be any faster than AES-GCM depending on your setup but the only way to know for sure is to test it on your own hardware, environment, and workload.
@jsone said in cant prep 2.6.0 pfsense openvpn for 2.7.0:
@jimp said in cant prep 2.6.0 pfsense openvpn for 2.7.0:
You don't need to manually assign a tunnel network in the overrides
for some bizar reason, it was (sometimes) assigning the client .5 or .6 so i had to use the tunnel network in the client override to force it to .2
The beauty of keeping the CSO entries generic is you don't have to know or care what address clients get. It doesn't matter. The server knows the client by its cert CN/username and will route things appropriately.
Currently it's not possible to install Plus directly but it's something we are working on now.
If your goal is to get to 23.05 though you should be able to upgrade to that directly from 2.6. I would still uninstall Squid first.
Steve
@stephenkwabena what does that mean??? Nobody can help you with out some info.. "No please" isn't info..
I would love nothing more than to help you figure out your problem... But without some info there is nothing anyone can do..
@TAC57 You will need the 2.6-RELEASE config before the update -- you can get it from the config history if you haven't pulled it already: https://docs.netgate.com/pfsense/en/latest/backup/restore-different-version.html
As for ZFS... yeah, it's a process. It's automated in Plus but that won't help you.
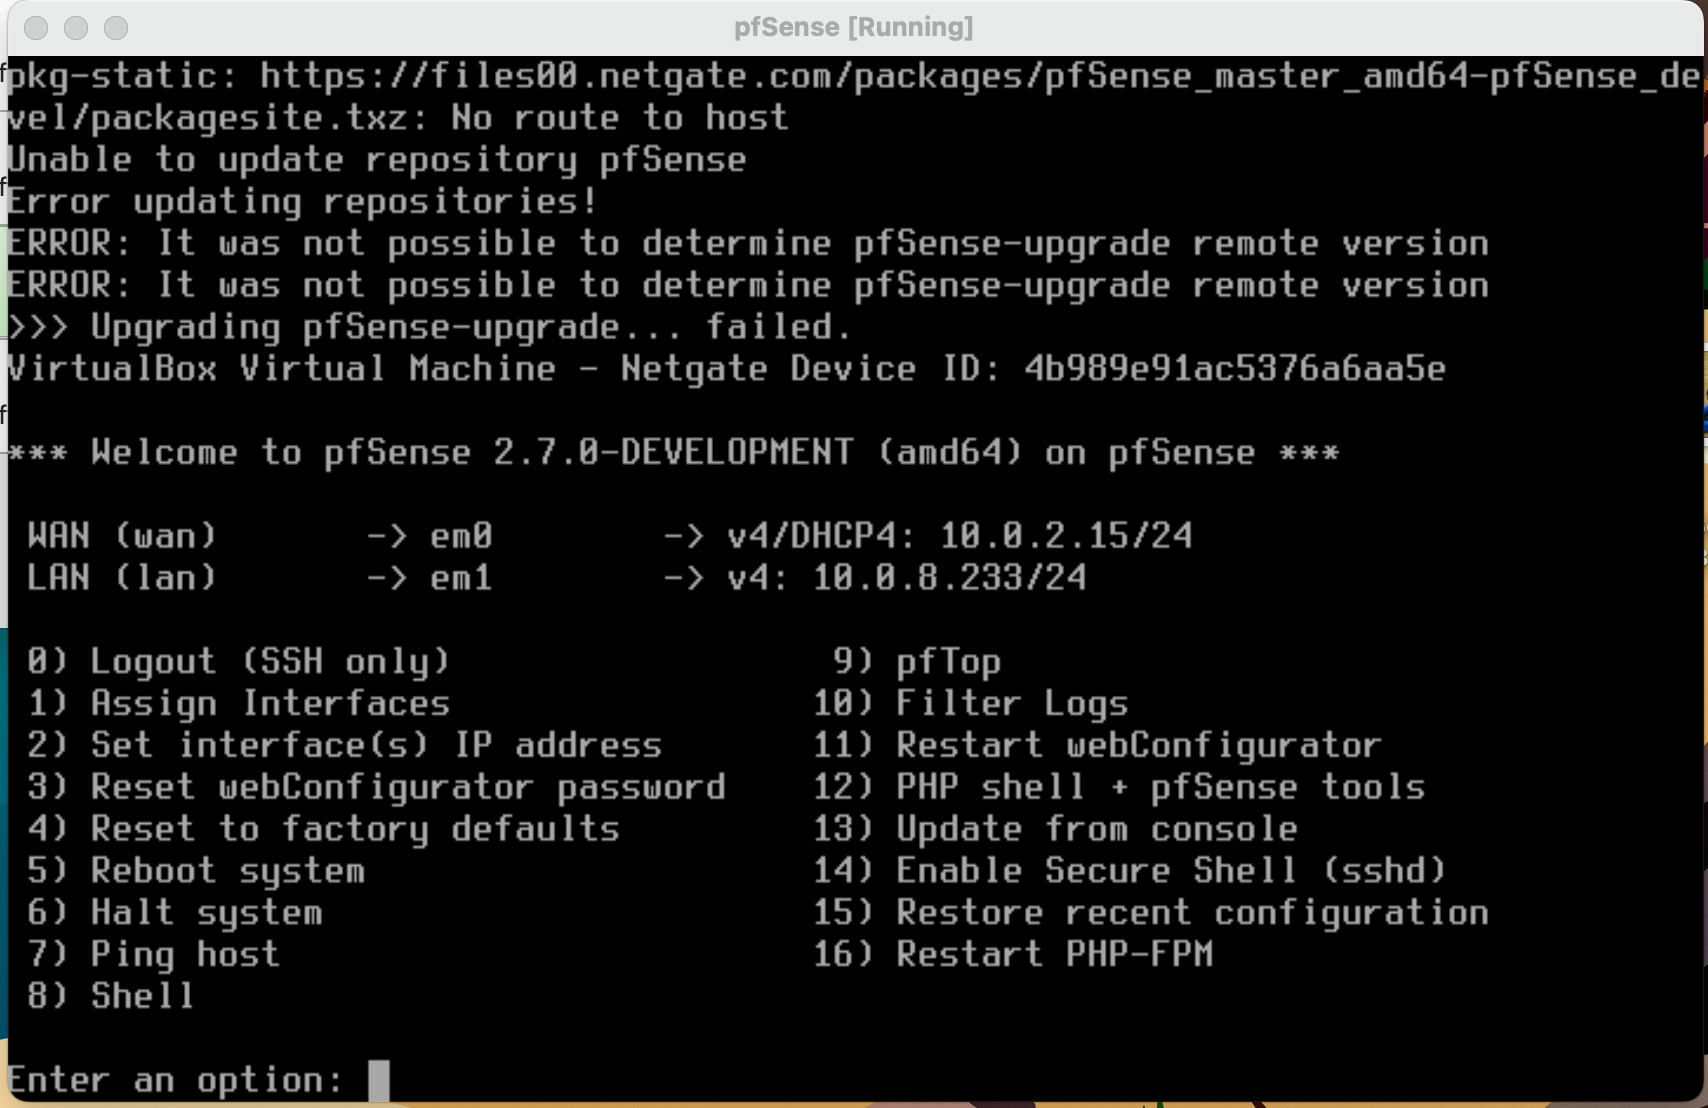
@Dobby_ I'll try again later...and later did it...got to bump up my VirtualBox VM memory for the next development...
[image: 1687051881172-screenshot-2023-06-17-at-8.24.31-pm.png]
Since today I was able to upgrade two times the 2.7
Devel version and now it is named 2.7 BETA and you
may be able to choose to upgrade directly from it
to 23.05.
[image: 1687025418576-2.7-beta-to-23.05-1.jpg]
[image: 1687025418605-2.7-beta-to-23.05-2.jpg]
@kiokoman Excellent. Thank you for the knowledge on the error code. I dont see it as much I can do to fix it and hopefully the new box with a J4125 CPU will do better. I believe its my Uncle Murphy showing up and I got a wonky CPU.
Fanless Soft Router Celeron J4125 Mini PC Quad Core 4x Intel i225 2.5G LAN HDMI VGA pfSense Firewall Appliance ESXI AES-NI
I'm using this one, it also have 8 gb/ram and 256gb/ssd