MultiWAN Failover Not Passing Data
-
I have a gateway group set-up so that if the primary WAN fails (Tier 1), the back-up WAN (Tier 2) activates. I'm trying to limit the amount of data that is used on the back-up WAN.
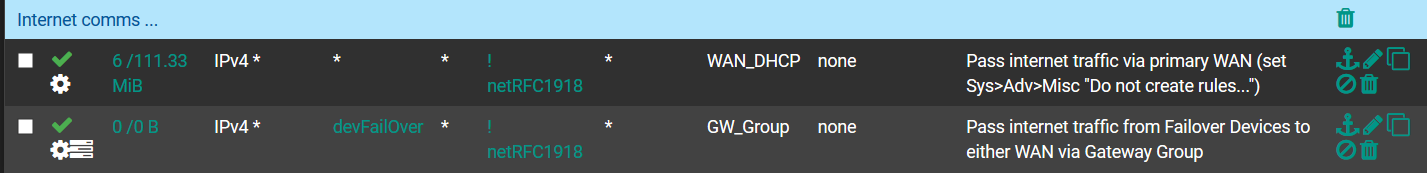
The gateway group is behaving as expected, but when the primary WAN fails it seems the firewall does not allow data from authorized LAN devices (devFailOver) to pass to the the gateway group. Below is a shot of my firewall rules.
So far, I figured out that :
-
when the primary WAN is up (WAN_DHCP), all LAN devices can pass through the gateway as expected.
-
in a failover condition, if I disable the first rule (which allows any LAN device to pass through to the primary WAN), then the authorized LAN devices (devFailOver) can pass through the gateway group to the internet just fine.
-
however, in a fail-over condition, if the first rule is enabled, the authorized LAN devices (devFailOver) can not pass through the gateway group to the internet
Note that under System > Advance > Misc, I have enabled "Do not create rules when gateway is down". I presume that when the primary WAN goes down, that that first rule "goes away". However, it behaves as though its still active.
-
-
I still don't know why the above firewall rules didn't work, but what did work was:
- flipping the rule order so that devices which are only allowed through the Tier 1 WAN gateway is the last rule
- enable Sys > Adv > Misc "Flush all states when a gateway goes down" was also needed for certain devices (i.e. VoIP phones) allowed through either gateway
Hello! It looks like you're interested in this conversation, but you don't have an account yet.
Getting fed up of having to scroll through the same posts each visit? When you register for an account, you'll always come back to exactly where you were before, and choose to be notified of new replies (either via email, or push notification). You'll also be able to save bookmarks and upvote posts to show your appreciation to other community members.
With your input, this post could be even better 💗
Register LoginPrivacy Policy · Cookie Policy