send packets out the same interface it arrived on
-
My questions seems rather an easy one but I couldnt make it work.
I have servers behind Netgate Firewall and two wan interfaces.
I want packets arriving from wan1 to leave again from wan1. Same goes with wan2.
I want packets arriving from wan2 to leave again from wan2.
In my case all packets regardless of their arriving interface, leave the inteface where default gw is.
Both modems I have are performing destination NAT.
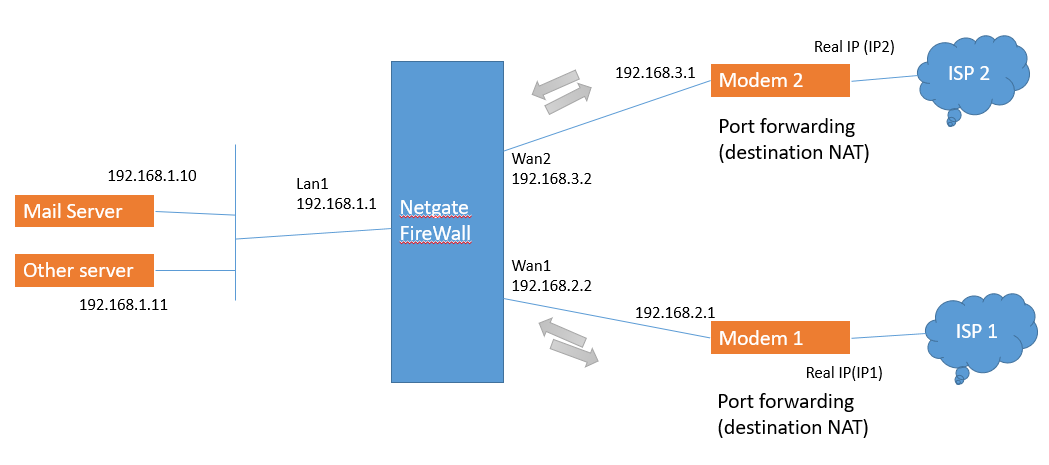
Any hint will be appreaciated.
-
@thetevfik said in send packets out the same interface it arrived on:
I want packets arriving from wan1 to leave again from wan1. Same goes with wan2.
I want packets arriving from wan2 to leave again from wan2.I guess, you're talking about responds packets on request from outside.
So that's the default behaviour in pfSense, it is controlled by the "reply-to" flag, which is added to any packet coming in on an interface which has a gateway is defined on. However, there are some requirements:- The rule allowing the respective access in pfSense must not be a floating rule.
- The rule allowing the respective access must not be a defined on an interface group.
So probably you have to check if these requirements are given on your pfSense.
-
Bull's-eye. The answer I was looking for. Thank you @viragomann very much
Hello! It looks like you're interested in this conversation, but you don't have an account yet.
Getting fed up of having to scroll through the same posts each visit? When you register for an account, you'll always come back to exactly where you were before, and choose to be notified of new replies (either via email, or push notification). You'll also be able to save bookmarks and upvote posts to show your appreciation to other community members.
With your input, this post could be even better 💗
Register LoginPrivacy Policy · Cookie Policy