No downstream/inbound traffic coming in
-
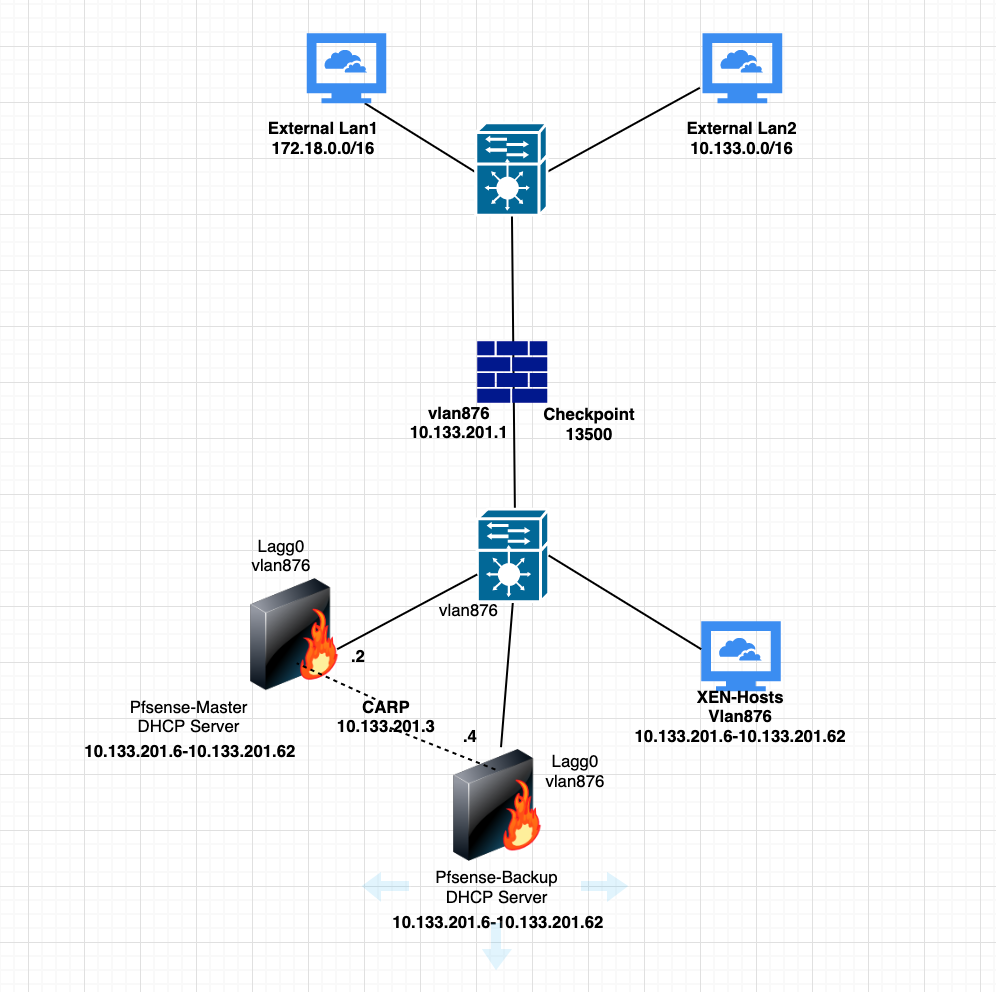
Hi All,
I have a problem where all external lans are unable to to access all the xen hosts using dhcp server with ip's 10.133.201.6 to 62, DHCP is working fine and all the vm's are leased. From the XEN hosts, i can reached all external LANS, with out a problem. My biggest issue is the inbound.
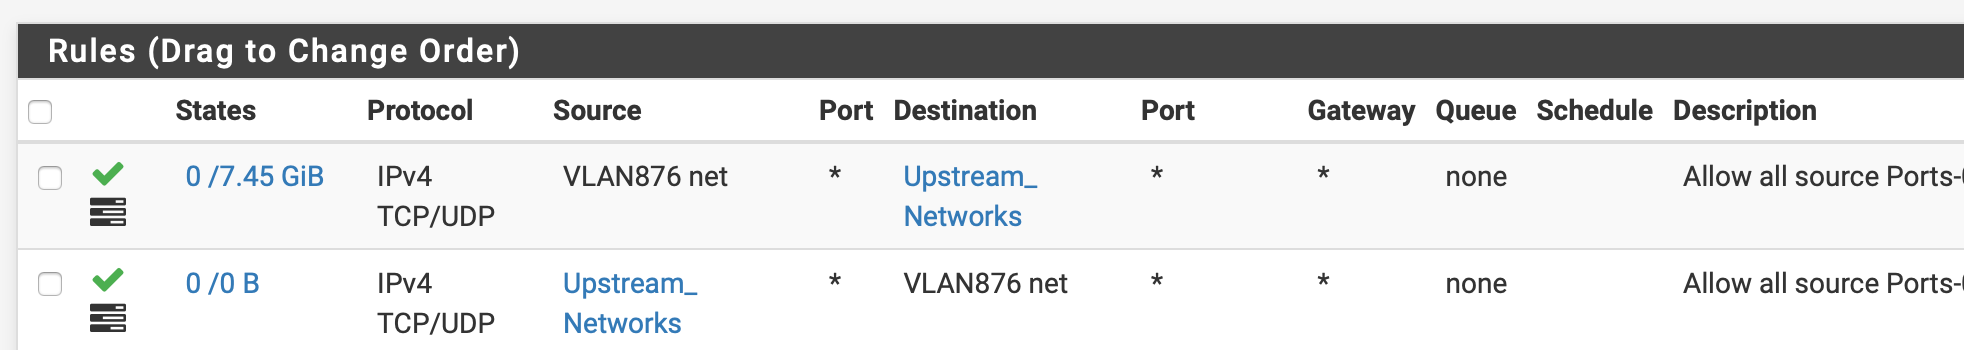
The rules on my vlan876 is as follows
External -> Vlan876net -> ANY
Vlan876net ->External Lan ->ANYonly upstream works. there are now any WAN requirements as this is an internal firewall and only acts as a DHCP server and nothing else.
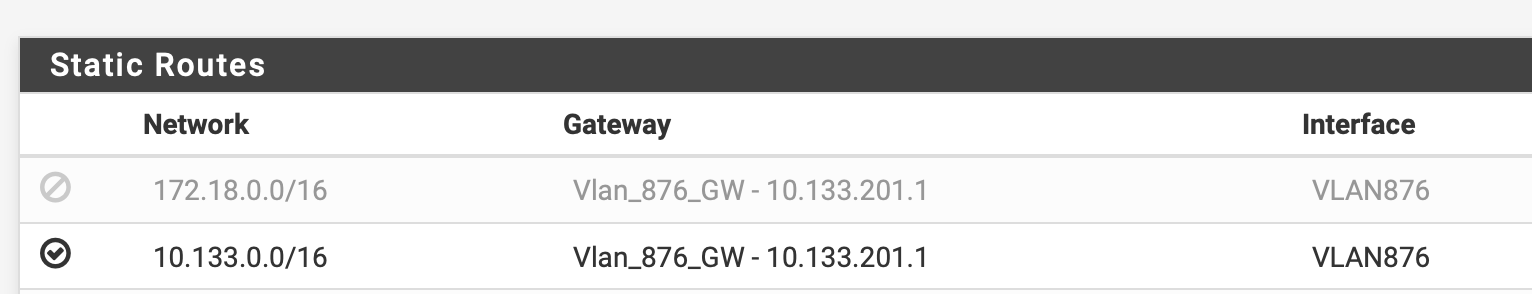
I'ved try playing with floating, static routes,1:1 and port forwarding without any success. currently, the pfsense is pointing the nexthop to the checkpoint fw interface - 10.133.201.1. And from what i observed from checkpoint fw logs, traffic is passing out the cp firewall but stops on the pfsense. From checkpoint FW, i can reach all the ip's and CARP of the pfsense interface and all of the xen host.
Setup:
on Pfsense
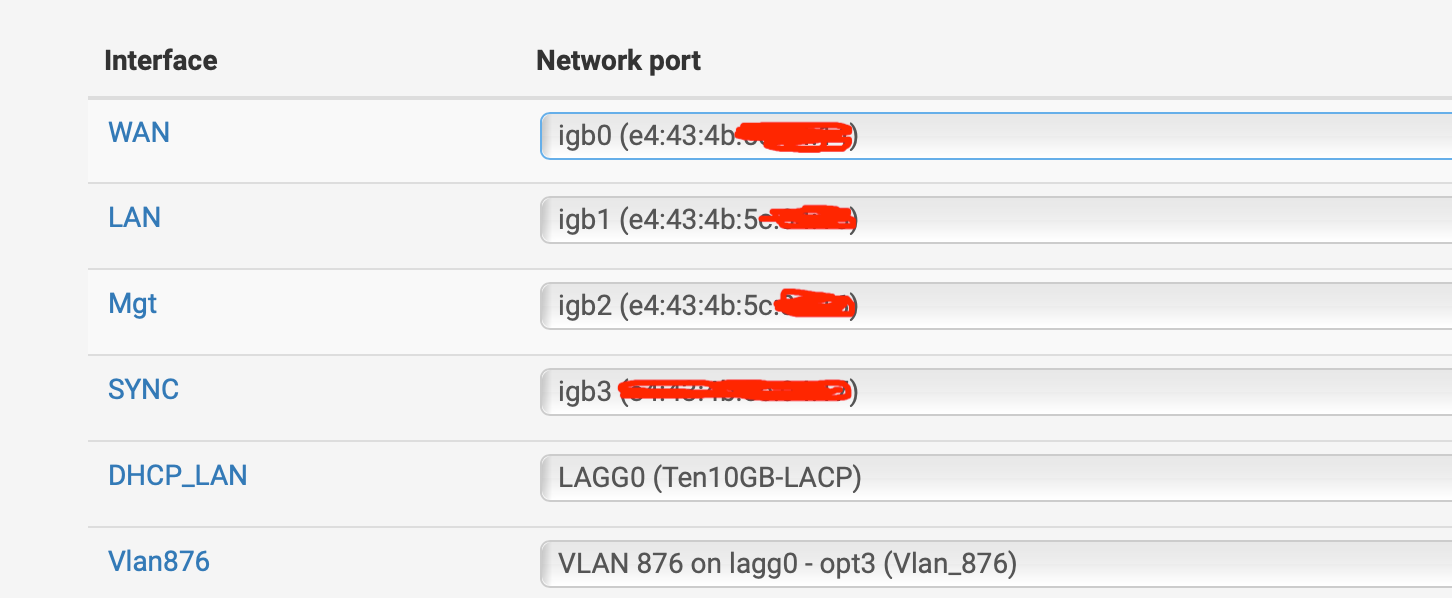
i have Lagg0(lacp) interface without ip as i believe is a physical connections only(traffic pass through). Vlan876 interface lies under the Lagg0. i have enabled the manual outbound NAT, in which all the vlan876 were able to connect to my external lans.The carp seems to be working fine as the node2 becomes a backup.
Here's my policy:
upstream routes:
Interfaces: wan and lan is just there without any physical connections:
appreciate if anyone point me on the right direction.
Regards.
-
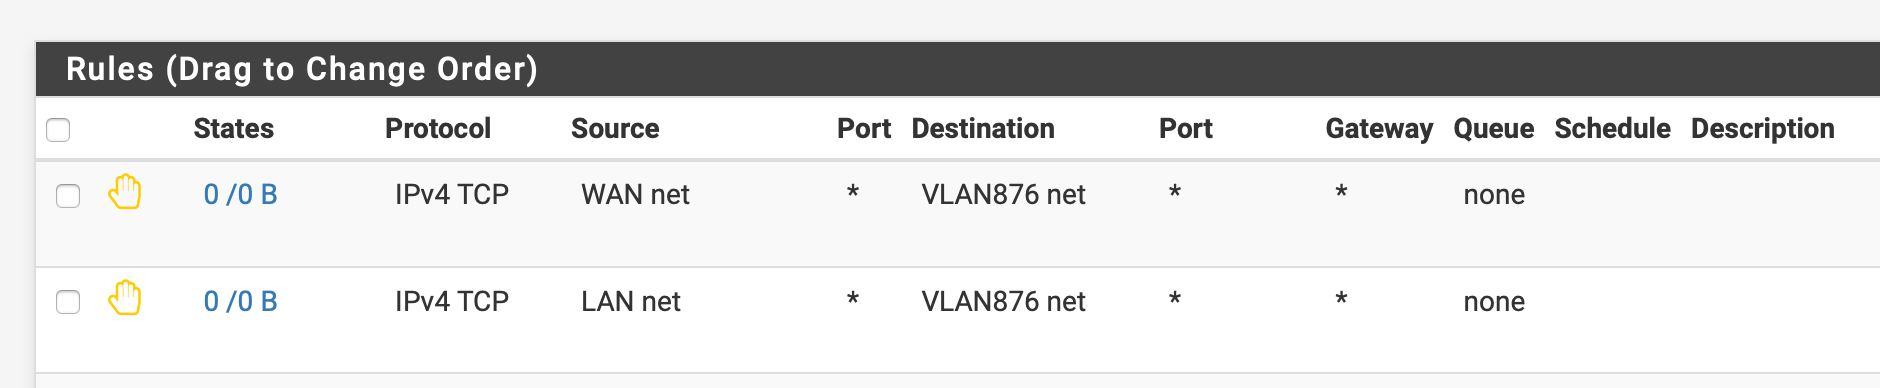
i'ved added two new reject rules on interface vlan876. still not working =(
Hello! It looks like you're interested in this conversation, but you don't have an account yet.
Getting fed up of having to scroll through the same posts each visit? When you register for an account, you'll always come back to exactly where you were before, and choose to be notified of new replies (either via email, or push notification). You'll also be able to save bookmarks and upvote posts to show your appreciation to other community members.
With your input, this post could be even better 💗
Register LoginPrivacy Policy · Cookie Policy