Netgate Discussion Forum
    • Categories
    • Recent
    • Tags
    • Popular
    • Users
    • Search
    • Register
    • Login
    Introducing Netgate Nexus: Multi-Instance Management at Your Fingertips.

    Sg-2100 vlan setup no internet

    Scheduled Pinned Locked Moved Firewalling
    8 Posts 2 Posters 2.2k Views 2 Watching
    Loading More Posts
    • Oldest to Newest
    • Newest to Oldest
    • Most Votes
    Reply
    • Reply as topic
    Log in to reply
    This topic has been deleted. Only users with topic management privileges can see it.
    • D Offline
      drummerboyj
      last edited by

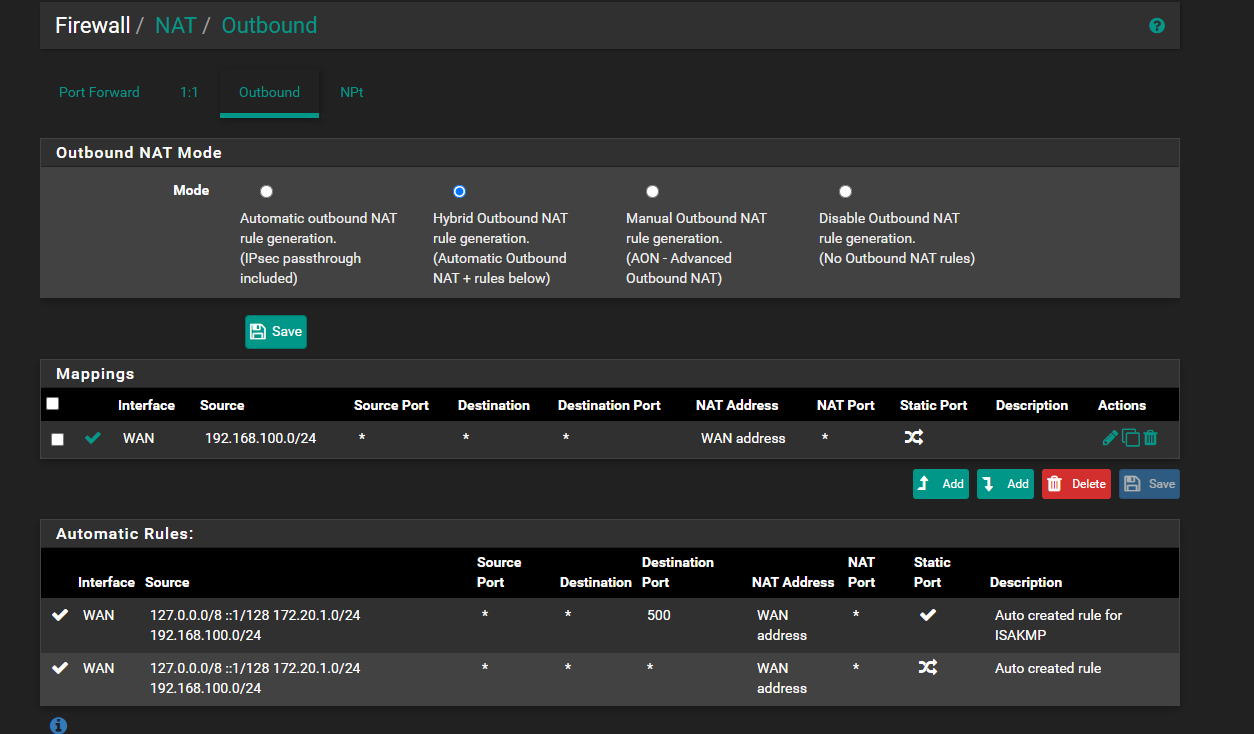
      I’ve followed the sg2100 documentation to the letter for setting up a vlan (after resetting to factory default) then I enabled the dhcp server and created firewall rules to allow lan to any on the correct interface. I checked the nat and the auto rules included the up address of the vlan but I created a new nat and saved as hybrid anyways and still no internet access on vlan. I am not an expert but I am not completely new to this either and I’ve been reading all over this forum for a couple weeks and have tried so many of the solutions I’ve seen suggested to others and nothing has worked I can only get internet access on the default lan. What am I missing? I am not double natted my setup is isp to cm1000 modem to netgate sg-2100 then using my pc and connecting to different ports to test eventually I want to connect my Cisco sg350 switch on one vlan and my WiFi ap on another vlan and a server on a 3rd vlan and leave one port on the default lan for connecting to the pfsense GUI. I can’t even get the first step of getting the vlans to connect to the internet so I reset everything to default and just tried to create a single vlan following every step of the documentation and connecting my pc and still no internet. Any help as to what I could possibly be missing would be amazing. Thanks

      SteveITSS 1 Reply Last reply Reply Quote 0
      • SteveITSS Offline
        SteveITS Rebel Alliance @drummerboyj
        last edited by

        Can you post your firewall rules for the VLAN interface, that allow traffic to the Internet? Have you tried pinging an IP (e.g. 8.8.8.8) vs. a web site (to rule out DNS)?

        To upgrade, select your branch in System/Update/Update Settings. When upgrading, allow 10-15 minutes to reboot, or more depending on packages, CPU, and/or disk speed.
        Only install packages for your version of pfSense.
        Upvote 👍 helpful posts!

        D 1 Reply Last reply Reply Quote 0
        • D Offline
          drummerboyj @SteveITS
          last edited by

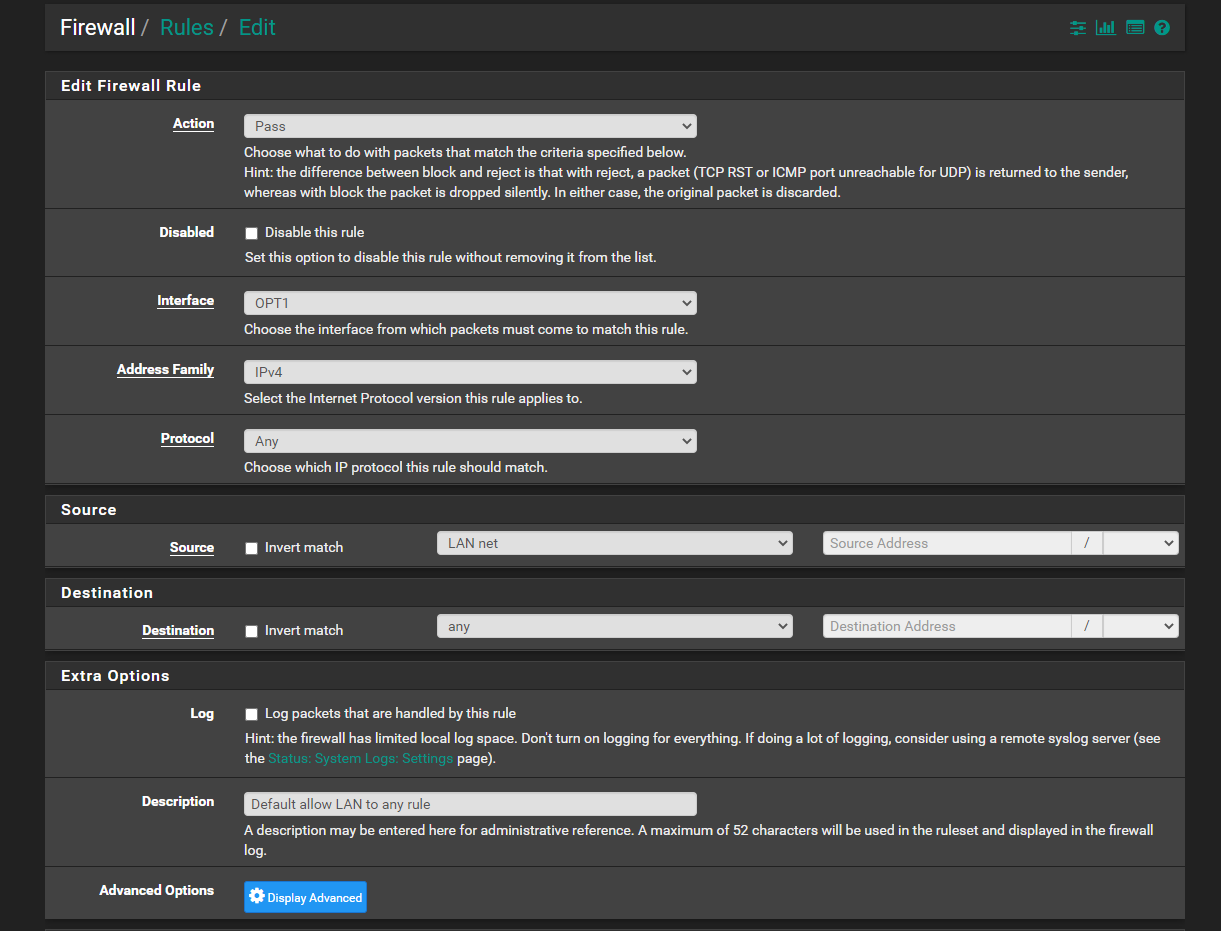
          @teamits i just tried pinging 8.8.8.8 and got ping transmit failed general failure. I copied the firewall rule from the existing lan and only changed the interface to be opt1 instead of lan. pfsense firewall rule.png
          D SteveITSS 2 Replies Last reply Reply Quote 0
          • D Offline
            drummerboyj @drummerboyj
            last edited by

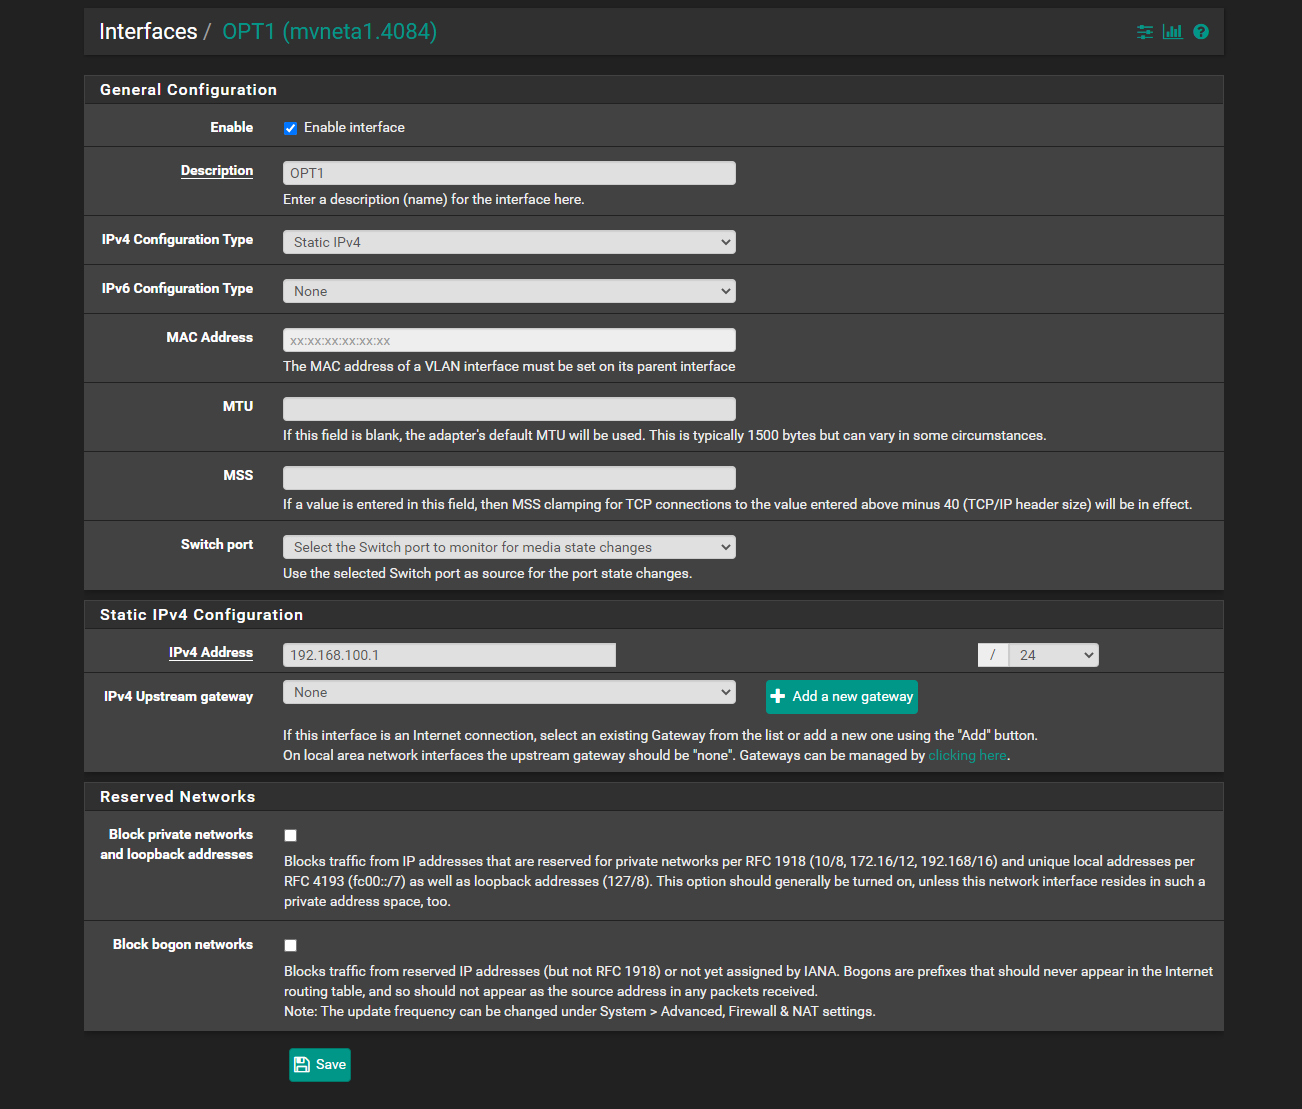
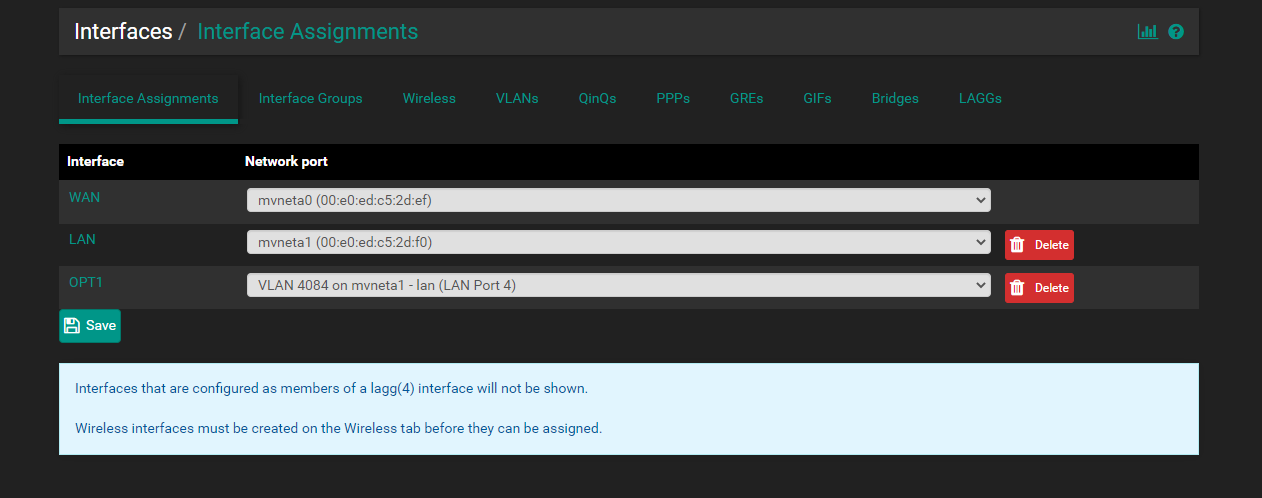
            more screenshots pfsense interface.png pfsense interface assignment.png pfsense nat outbound.png

            1 Reply Last reply Reply Quote 0
            • SteveITSS Offline
              SteveITS Rebel Alliance @drummerboyj
              last edited by

              In the firewall rule you have "source" as "LAN net" not "OPT"

              To upgrade, select your branch in System/Update/Update Settings. When upgrading, allow 10-15 minutes to reboot, or more depending on packages, CPU, and/or disk speed.
              Only install packages for your version of pfSense.
              Upvote 👍 helpful posts!

              D 1 Reply Last reply Reply Quote 0
              • D Offline
                drummerboyj @SteveITS
                last edited by

                @teamits good catch I must have missed that on my attempt this morning but still the same issue when that is set to opt 1 net and I know ive set that properly in previous attempts with the same issue. with that set to opt 1 net i still get the general ping failure to 8.8.8.8

                SteveITSS 1 Reply Last reply Reply Quote 0
                • SteveITSS Offline
                  SteveITS Rebel Alliance @drummerboyj
                  last edited by

                  Can you ping 192.168.100.1 from a device on OPT1?

                  Is the tag right in Interfaces/Switches? (steps 15-26 here https://docs.netgate.com/pfsense/en/latest/solutions/netgate-2100/switch-overview.html)

                  You can try pinging from the pfSense under the Diagnostics menu, as well.

                  To upgrade, select your branch in System/Update/Update Settings. When upgrading, allow 10-15 minutes to reboot, or more depending on packages, CPU, and/or disk speed.
                  Only install packages for your version of pfSense.
                  Upvote 👍 helpful posts!

                  D 1 Reply Last reply Reply Quote 0
                  • D Offline
                    drummerboyj @SteveITS
                    last edited by

                    @teamits and that was it. its working now I had turned off tagging on 5 earlier on opt 1 because i saw that the default lan didnt have 5 tagged. Probably everytime i did the setup there would always be one step i messed up because on other attempts i had it tagged properly. anyways its working now thank you!

                    1 Reply Last reply Reply Quote 0
                    • First post
                      Last post
                    Copyright 2026 Rubicon Communications LLC (Netgate). All rights reserved.
                    Privacy Policy · Cookie Policy