Netgate Discussion Forum
    • Categories
    • Recent
    • Tags
    • Popular
    • Search
    • Register
    • Login
    Introducing Netgate Nexus: Multi-Instance Management at Your Fingertips.

    Can't Hit Port Forward From Inside LAN

    Scheduled Pinned Locked Moved General pfSense Questions
    5 Posts 3 Posters 1.1k Views 3 Watching
    Loading More Posts
    • Oldest to Newest
    • Newest to Oldest
    • Most Votes
    Reply
    • Reply as topic
    Log in to reply
    This topic has been deleted. Only users with topic management privileges can see it.
    • Z
      Zxvrra
      last edited by Zxvrra

      I work as a network engineer but am not particularly familiar with pfsense.

      I have a port forward from my Public IP:80 ---->192.168.1.5:80, but I can't figure out why if I type in my public IP address from inside the LAN I end up at 192.168.1.1:80 instead. It works fine outside the LAN. I would assume maybe pfsense is not forwarding the traffic out to the internet and coming back in maybe it is taking a quicker route without going through the WAN gateway or something. If anyone has any ideas please let me know!

      V 1 Reply Last reply
      Reply Quote 0
      • V
        viragomann @Zxvrra
        last edited by

        @zxvrra
        The port forwarding does not work from inside, cause the NAT rule is defined on the WAN interface. So it only is applied to traffic coming in on WAN.

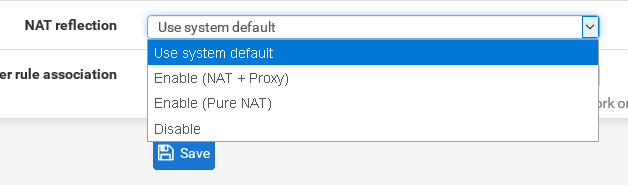
        If you want to access the public IP from inside you can enable NAT reflection in the NAT rule. If client and server are connected to the same network interface you might have to use "NAT + proxy" mode.

        If you use a host name to access the server, it's recommended to add a DNS override for it instead.

        SteveITSS 1 Reply Last reply
        Reply Quote 0
        • SteveITSS
          SteveITS Galactic Empire @viragomann
          last edited by

          Also, in System/Advanced/Firewall & NAT ensure reflection is enabled in general.

          To upgrade, select your branch in System/Update/Update Settings. When upgrading, allow 10-15 minutes to reboot, or more depending on packages, CPU, and/or disk speed.
          Only install packages for your version of pfSense.
          Upvote ๐Ÿ‘ helpful posts!

          V 1 Reply Last reply
          Reply Quote 0
          • V
            viragomann @SteveITS
            last edited by

            @steveits said in Can't Hit Port Forward From Inside LAN:

            Also, in System/Advanced/Firewall & NAT ensure reflection is enabled in general.

            This enables NAT reflection globally, so that it's enabled by default in all NAT rules:
            785396dd-0aba-48db-ba0f-fa47d8ac5033-grafik.png

            Possibly that is not always desired and it's not necessary to enable it for a single forwarding rule.

            SteveITSS 1 Reply Last reply
            Reply Quote 0
            • SteveITSS
              SteveITS Galactic Empire @viragomann
              last edited by

              @viragomann said in Can't Hit Port Forward From Inside LAN:

              not necessary to enable it for a single forwarding rule

              Did not realize that, thanks.

              To upgrade, select your branch in System/Update/Update Settings. When upgrading, allow 10-15 minutes to reboot, or more depending on packages, CPU, and/or disk speed.
              Only install packages for your version of pfSense.
              Upvote ๐Ÿ‘ helpful posts!

              1 Reply Last reply
              Reply Quote 0

              Hello! It looks like you're interested in this conversation, but you don't have an account yet.

              Getting fed up of having to scroll through the same posts each visit? When you register for an account, you'll always come back to exactly where you were before, and choose to be notified of new replies (either via email, or push notification). You'll also be able to save bookmarks and upvote posts to show your appreciation to other community members.

              With your input, this post could be even better ๐Ÿ’—

              Register Login
              • First post
                Last post
              Copyright 2026 Rubicon Communications LLC (Netgate). All rights reserved.
              Privacy Policy · Cookie Policy