ipsec tunnel beetwen Fortigate and pfsense
-
Hello guys.
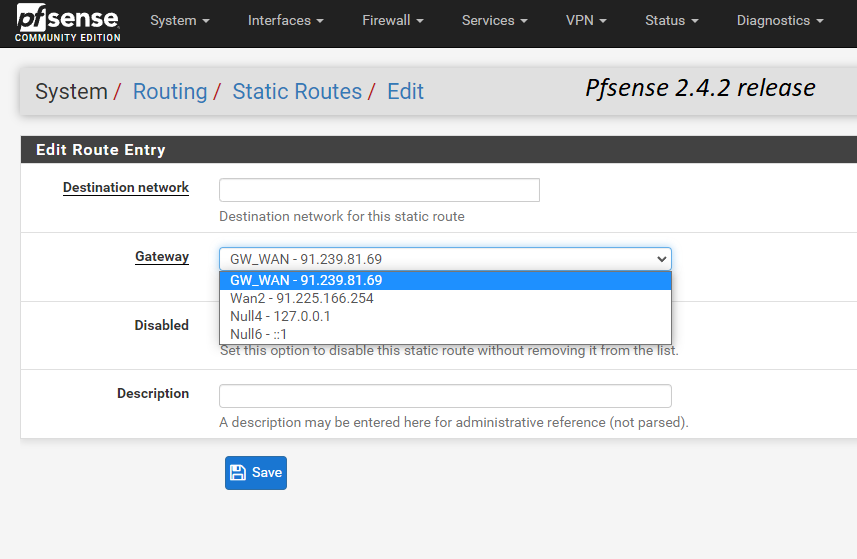
Got ipsec tunnel beetwen them.Can't find on pfsense side how to add route to LAN behind Fortigate fireweall.
Fortigate allows adding route through the ipsec tunnel.So I did it.
Pfsense doesn't got IPsec interfaces,so I can't add route through the tunnel.Therefore my ping requests from LAN behind Fortigate are reaching pfsense,but echo replies don't know how to back home.
Is there a way to add route through Ipsec tunnel on pfsense?
-
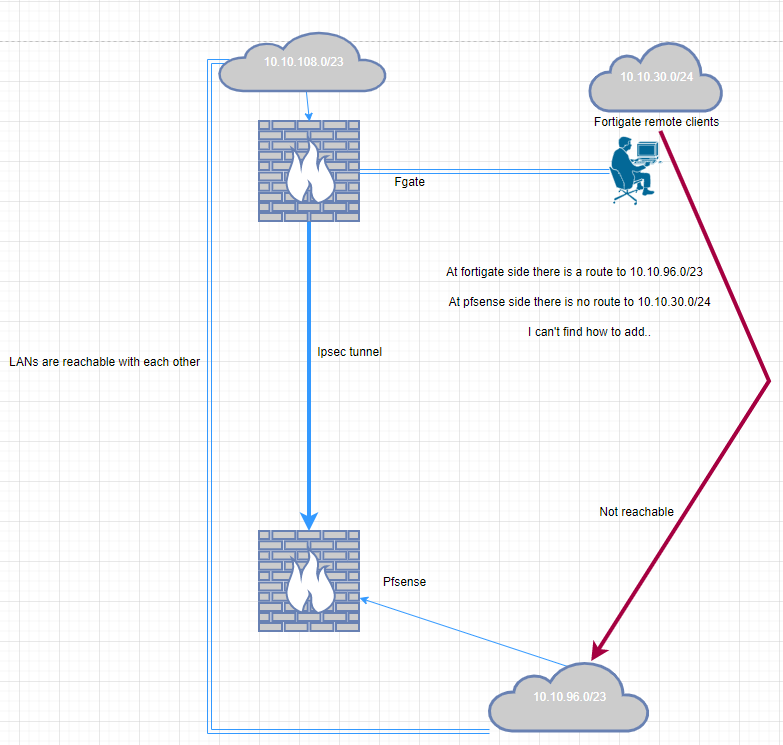
There are remote clients(10.10.30.0/24) who connect to Fortigate remotely(vpn).
Exactly this network should be known by pfsence to work with.But,I can't add it as a route through pfsense ipsec channel on pfsense side. -
Do you have the lan as a P2? This seems pretty straightforward unless I am missing something. I have a couple fortigates I connect to and similar situations as this.
-
@cswroe said in ipsec tunnel beetwen Fortigate and pfsense:
Do you have the lan as a P2? This seems pretty straightforward unless I am missing something. I have a couple fortigates I connect to and similar situations as this.
Hello.Didn't get about P2...
Well,if I use NAT at Fortigate,its ok.Packets are NATed and traffic flows fine between 10.10.30.0/24 and 10.10.96.0/23
But I want to get functionality without NAT.Can you check if possible..How to add route through ipsec at pfsense side.
Diagram is here.
-
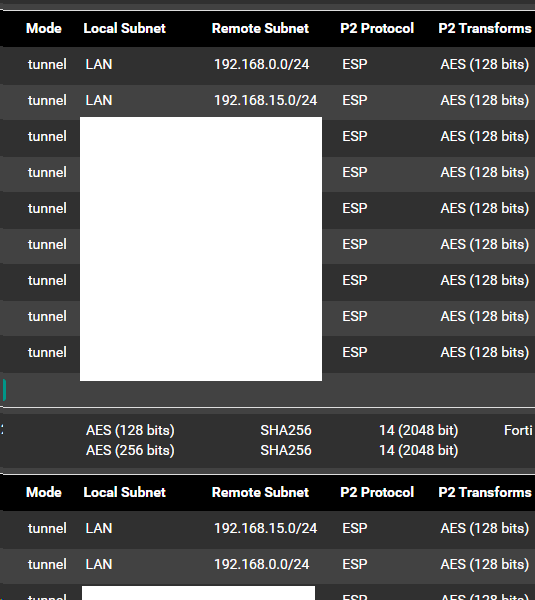
You should have P2 entries under the P1 VPN entry to establish the far-end networks.
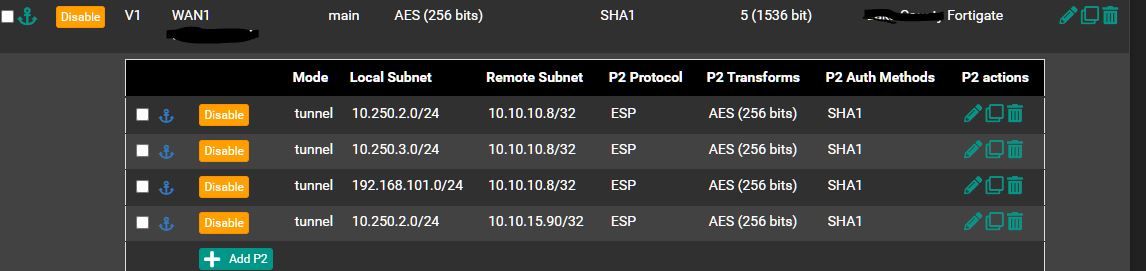
You will need one on the pfsense for 10.10.30.0/24 local subnet
There will be a similar entry on the Fortigate side for the 10.10.96.0/23https://docs.netgate.com/pfsense/en/latest/vpn/ipsec/configure.html#phase-2-settings
-
It is done.
Thanks for your help.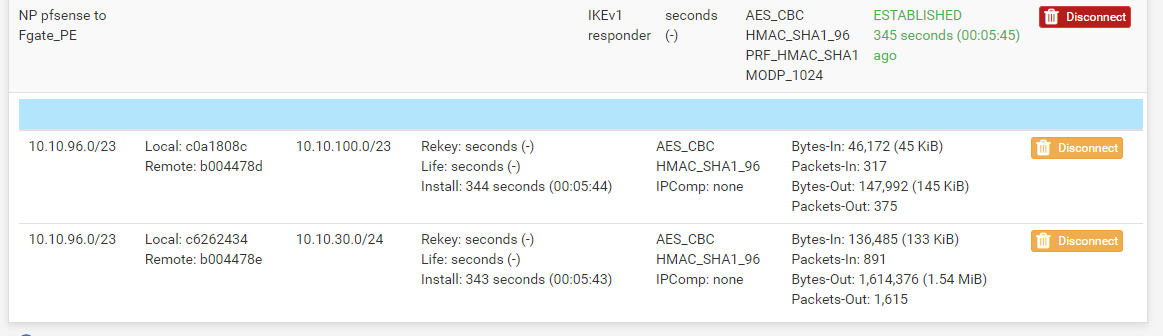
-
@cswroe hi there
do I understood it correctly that pfsense doesn't need to have configured static routes to route traffic between opposite LANs as in regular network equipment (cisco fortinet etc.)?
-
@boi As long as pfsense knows what to do what the IP requested (P2 entry) and there are firewall rules permitting it, there should be no need for a static route.
-
@cswroe thanks for quick reply I appreciate it.
maybe you could give a hint regarding load balancing algorithm in case with specific remote LAN reachable behind two separate tunnels? will it be ECMP?

Hello! It looks like you're interested in this conversation, but you don't have an account yet.
Getting fed up of having to scroll through the same posts each visit? When you register for an account, you'll always come back to exactly where you were before, and choose to be notified of new replies (either via email, or push notification). You'll also be able to save bookmarks and upvote posts to show your appreciation to other community members.
With your input, this post could be even better 💗
Register LoginPrivacy Policy · Cookie Policy