How to: HA with multi WAN and LCAP
-
Hi,
Can someone please give me some guidance on this:
I want to setup a HA scenario with 2x PFSence firewalls, with a single WAN uplink to Each PFSense firewall. The ISP will setup LACP, on 2 switches in the same virtual chassis on their two switches for failover. They say I need to have MC-LAG capabilities, but don't see such an option in PFSense. Is this perhaps a setting, but named differently?
The idea is, that if either firewall is offline, or either Uplink is offline, internet connectivity still works.
See the following diagram of what I have in mind.
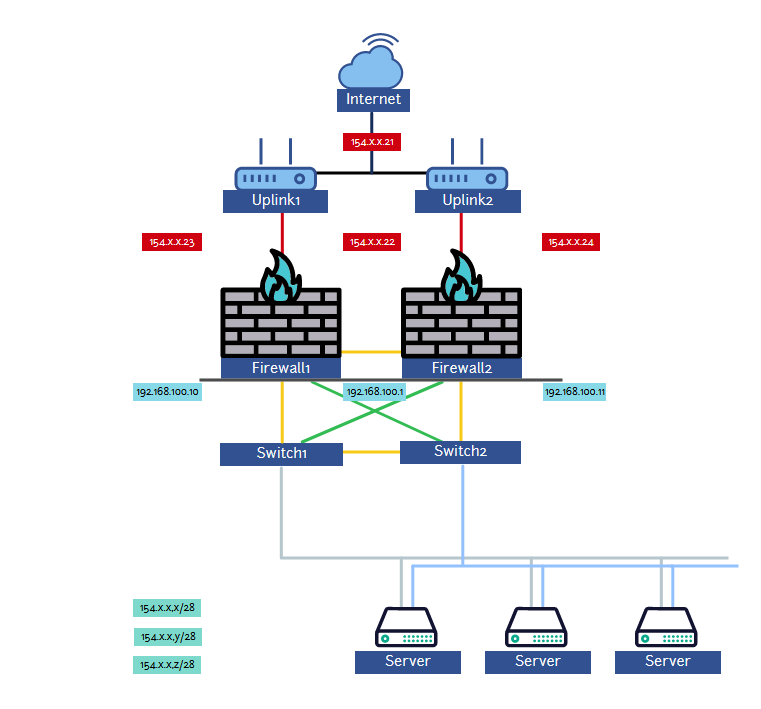
I had a look at the following article,but don't have the extra switches they talk about, and thus not sure how to setup PFSense on the two Firewalls
https://docs.netgate.com/pfsense/en/latest/recipes/high-availability-multi-wan.htmlWhat I want to achieve:
- high availability so that if either of the ISP uplinks, or our PFSense firewalls, or our own L3 switches were to go down, everything still works.
- We use OpenVPN, and OpenVPN needs to automatically work on the active / Master firewall. I guess this will be due to the floating IP address between the 2 firewalls?
- We use HAProxy to expose to Virtual Machines to the internet. HAProxy also need to have high availability, which I guess will also work with the floating IP
-
Can anyone give some pointer on this?
Hello! It looks like you're interested in this conversation, but you don't have an account yet.
Getting fed up of having to scroll through the same posts each visit? When you register for an account, you'll always come back to exactly where you were before, and choose to be notified of new replies (either via email, or push notification). You'll also be able to save bookmarks and upvote posts to show your appreciation to other community members.
With your input, this post could be even better 💗
Register LoginPrivacy Policy · Cookie Policy