RADIUS during failover
-
We have a Radius authentication server relationship setup with a Windows server NPS server, which works well.
But we also have dual WAN for failover, during failover the authentication breaks due to the public IP changing, can NPS be set up with multiple IPs or is it better to create separate Client profile's during a failover?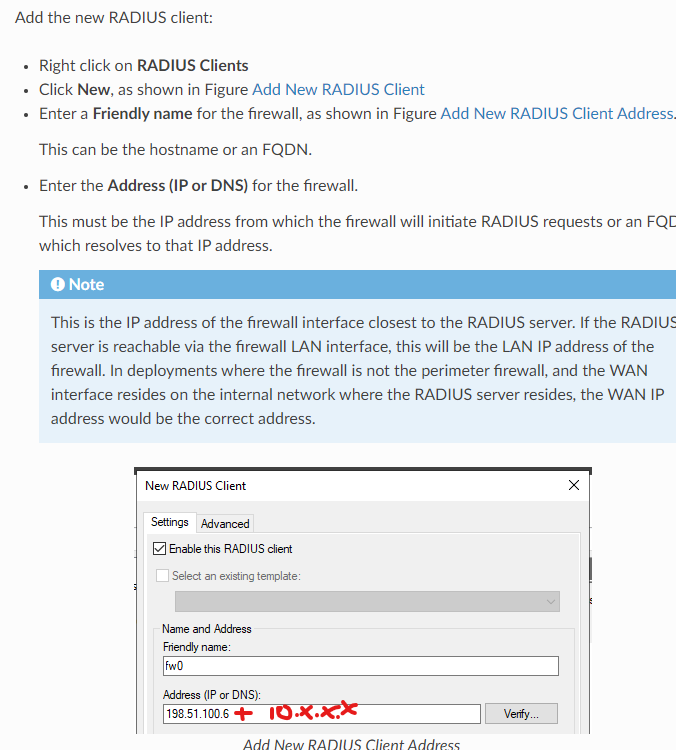
Scenario 1
Firewall \ WAN IP 1 -> NPS Client IP =WAN IP = 1 + 2
Failover
Firewall\WAN IP 2 - > NPS CLient IP =WAN IP = 1 + 2
(This does not seem possible)Scenario 2
Firewall \ WAN IP 1 -> NPS Client IP =WAN IP = 1
Failover
Firewall\WAN IP 2 - > NPS CLient IP =WAN IP = 2
Copyright 2026 Rubicon Communications LLC (Netgate). All rights reserved.
Privacy Policy · Cookie Policy
Privacy Policy · Cookie Policy