Longstanding FreeRADIUS EAP-TLS security bug on validating client certificate common name
-
I figured a screenshot would be easiest:
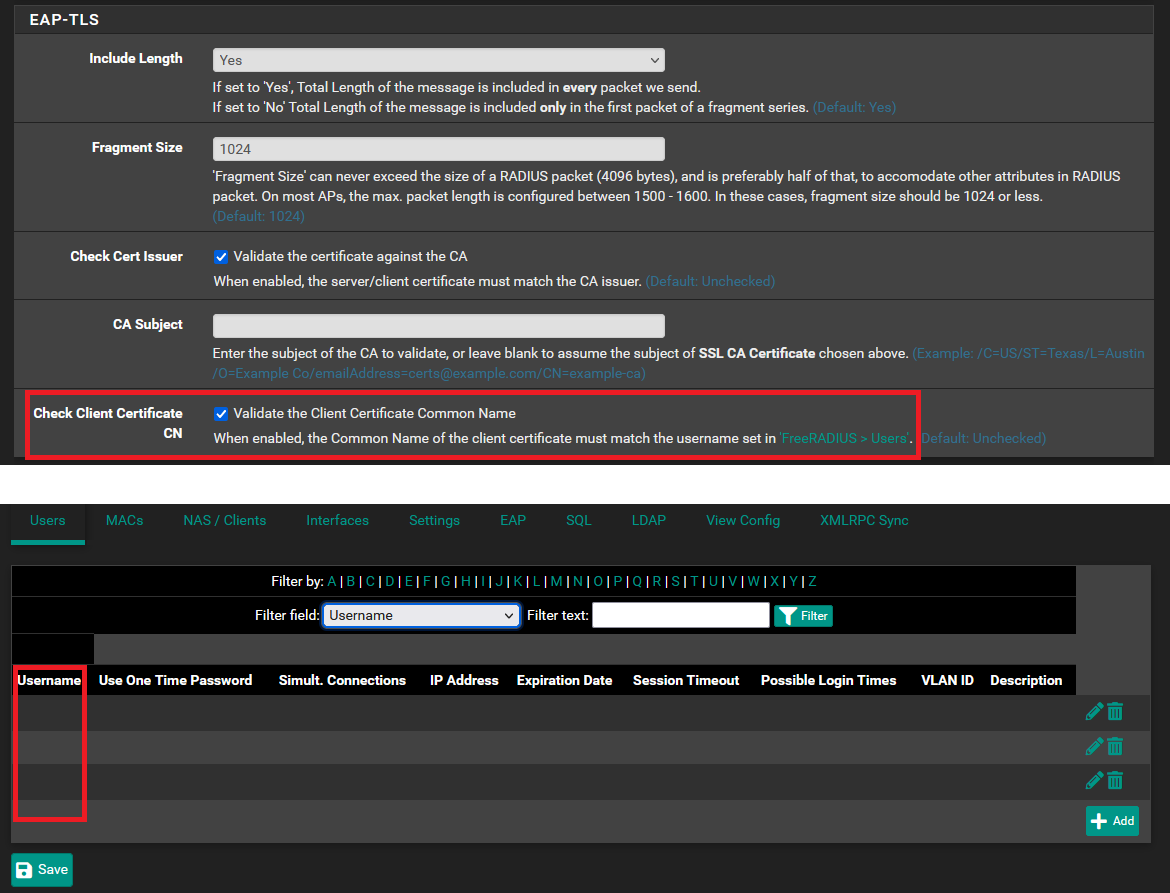
Basically, the "Validate the Client Certificate Common Name" checkbox in the EAP-TLS section does nothing. I can delete all users (or rename the username field to gibberish), and wireless devices can still connect to the WLAN. I presume that no validation/comparison is done to see if the Common Name that the client presents == the Username listed in "Users" in the FreeRADIUS package.
Thank you for your time.
-
Also seeing this bug, anyone know if theres any updates on this?
Edit: Looks like this is also known about here:
https://redmine.pfsense.org/issues/11054 -
@jamesg246 said in Longstanding FreeRADIUS EAP-TLS security bug on validating client certificate common name:
Also seeing this bug, anyone know if theres any updates on this?
Edit: Looks like this is also known about here:
https://redmine.pfsense.org/issues/11054I haven't seen any updates both in this thread and on the Redmine ticket. I linked the Redmine issue in the first line of the original post, btw.
Also updated the Redmine issue showing it is still broken in 2.7.2 with FreeRADIUS package 0.15.10_1.
I hope the screenshot makes it clear to understand the behavior we're talking about that is broken. It's sorta hard to follow in the bug report.
-
@Finger79 I remember running into this when they fixed it, but I did notice recently not working again.
I recall when they fixed it, because I was working without local users to validate the cn again, and then it broke.. Then I created them and working... But some recent thing I was doing I didn't have a user created and it worked..
I will try and add my 2 cents to the redmine, because I do believe it is currently not working again.. I have no users, have cn set to be check - and they auth, so clearly its not validating because there is nothing to validate against, etc..
its currently not working in 23.09.1, I was just going to wait to see what 24.03 brings.. Since its not really a big concern for me.. But I can see where it could be..
edit: so don't forget will put this here.. See I don't have a johnsphone user, and cn set to validate.. But it still auths just fine

-
F Finger79 referenced this topic on
-
Has this been fixed? I have the same problem in 24.03 and 0.15.10_2
-
@sltadm said in Longstanding FreeRADIUS EAP-TLS security bug on validating client certificate common name:
Has this been fixed? I have the same problem in 24.03 and 0.15.10_2
Nope, hasn't even been acknowledged. It's a minor security vulnerability.
The Redmine bug report is linked in this thread.
-
@Finger79 Thx for the info.
-
Can this security vulnerability get some love please?
-
Confirmed still an issue as of May 2025 with pfSense CE 2.8.0 and FreeRADIUS package version 0.15.14
I also updated the Redmine bugtracker: https://redmine.pfsense.org/issues/11054
Can this security vulnerability please get some attention? Wi-Fi supplicants are able to join an 802.1x WPA2-Enterprise network without the username in the client certificate validated at all.
-
Confirmed still an issue as of August 2026 with pfSense CE 2.9.0 and FreeRADIUS package version 0.16.4_1
I also updated the Redmine bugtracker: https://redmine.pfsense.org/issues/11054
Can this security vulnerability please get some attention? Wi-Fi supplicants are able to join an 802.1x WPA2-Enterprise network without the username in the client certificate validated at all.
-
Does anyone know why so many years go by with not even an acknowledgement from dev or staff? The Redmine bug hasn't been updated either except I do a yearly post testing it. It's still assigned to a much older version of pfSense, and I don't have the permissions to edit the Redmine issue so that it applies to 2.9.0 and is unresolved.
Also, if anyone knows where the source code is (GitHub?) for the FreeRADIUS package, maybe I can take a look at the code and find the bug. I'm usually really good at fixing things even if I don't have, say, PHP experience at the moment.
-
hey there! You sure it's not already fixed? At least the button has to do something because when I tried to get wifi device authentication working last week I had to disable this function for it to work :)
So I'm not totally sure but I think you have either server certs you can create in pfsense (which dont work because the server certs miss the correct usage embedded into the license for usage as wifi device certs?) or you can create client certs which can be either user certs for wifi or device certs for wifi.
At least I got device certs working if the client cert has the correct domain name included (like devicename.domain.com) in the common name and by installing both the CA cert and the device (client) cert into the "computer" trusted certs I was able to connect my laptop without needing users (using EAP-TLS). -
@sltadm said in Longstanding FreeRADIUS EAP-TLS security bug on validating client certificate common name:
hey there! You sure it's not already fixed? At least the button has to do something because when I tried to get wifi device authentication working last week I had to disable this function for it to work :)
So I'm not totally sure but I think you have either server certs you can create in pfsense (which dont work because the server certs miss the correct usage embedded into the license for usage as wifi device certs?) or you can create client certs which can be either user certs for wifi or device certs for wifi.
At least I got device certs working if the client cert has the correct domain name included (like devicename.domain.com) in the common name and by installing both the CA cert and the device (client) cert into the "computer" trusted certs I was able to connect my laptop without needing users (using EAP-TLS).Howdy! I just double-checked, and my config is still the same as in the screenshots in the OP. The checkbox is still checked, and in "Users," I can delete the users and my phones, iPad, laptops will still connect. Or I can rename the username to gibberish, and it'll still pass and allow them to connect to the network.
-
@Finger79 That's a bummer! I still have lots of client user certs and this would definitely be a an improvement however with me now being forced to disabled it to have device certs working I couldn't make use of it anyway...
If there wasn't a link to the user management next to that checkbox I'd say it's a wrong description and it's actual for device certs (and I'm doing something wrong) since if it's about checking if a local user exists in the pfsense why'd it matter for device certs if I have that function activated or not?... -
Do you guys know why literal years of silence in both this thread as well as the Redmine issue go by without a single acknowledgement from staff/developers? I'm trying to be patient and polite, but I feel like 2, 3+ years is a bit over-the-top.
The Redmine ticket still shows like 2.4.4 and Assigned, when it should be unassigned and changed to 2.9.0 for more visibility.
I've been a staunch supporter of pfSense for decades now and bought the t-shirts and polo shirt and give plenty of word of mouth. The silence kills me.

Privacy Policy · Cookie Policy