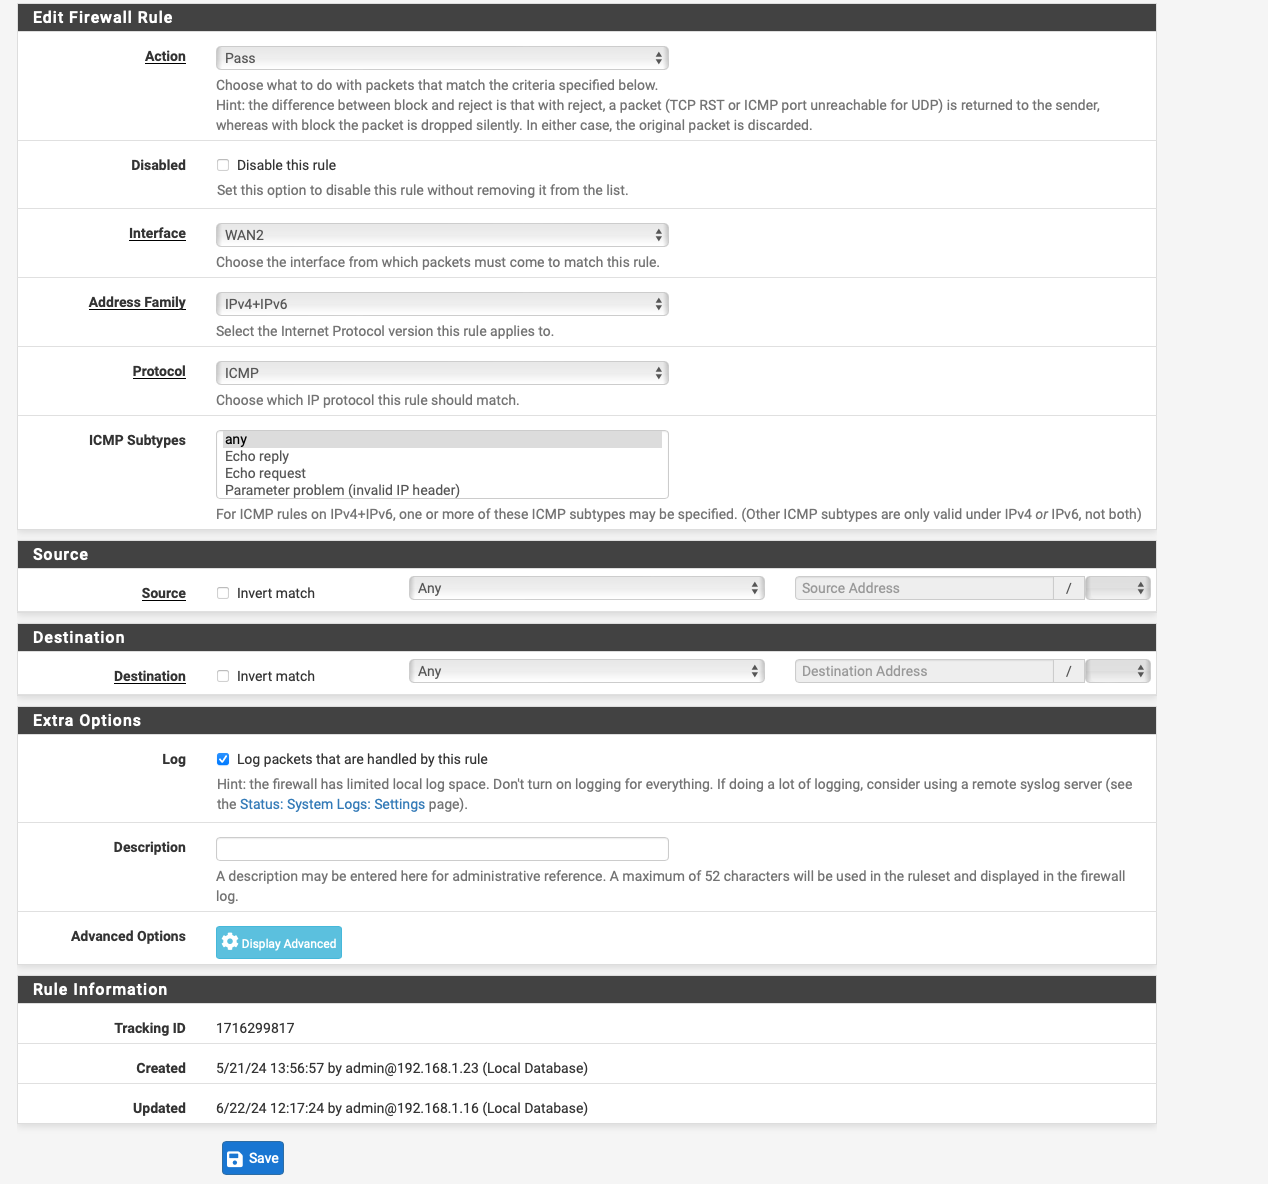
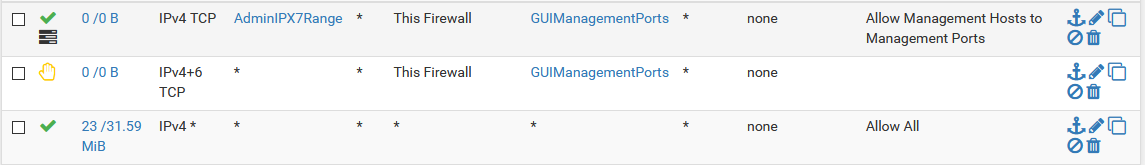
• Good GUI Port Numbers

    webGUI port https gui access
    9
    0 Votes
    9 Posts
    442 Views
    GertjanG
    @JonathanLee said in Good GUI Port Numbers: It’s the name applied in advanced settings for the firewall. Yours doesn’t do that ? I've my own rented domain name for my pfSense LAN networks. I use this domain name, let's call it "my-own-company.net" mostly internally. As this domain name does exist 'on the Internet', I rent it after all, I can easily about a (wild card) certificate. acme.sh using the most simple setup. I also rent some data center based servers, and some of them do the domain name server (DNS) handling for all my domain names. So, basically, no more DDNS hassle for me, as I became my own DDNS supplier. So i know where to find the admin if needed (its me). My ISP gives me static WAN IPv4s, and semi static IPv6 prefixes, so live is fine, as if DNS goes down, I know my IPv4 ^^ (my IPv6 is a bit harder). One pfSense to handle the ip/port NATting while IPv4 is still supported, and a simple firewall rule for IPv6, and done.
  • 0 Votes
    107 Posts
    44k Views
    JonathanLeeJ
    Great job, and you also learned port forwarding, ACL ordering, alias creation and much more. I love this forum you can learn so much. Now you just need a OpenVPN configured with a NAS server for private cloud use
  • 0 Votes
    7 Posts
    2k Views
    stephenw10S
    Yup that's a fun* one! More than 4 vmx NICs in esxi changes the PCI device ordering. Crazy.
  • WebGUI slow on IPv6 on WAN

    webGUI ipv6 gui access slow speed wan wan on vlan
    4
    0 Votes
    4 Posts
    2k Views
    GertjanG
    I tested my IPv6 access : I introduced a firewall rule on my HENET interface : [image: 1602092020877-32f30acb-b7d8-476a-bfd3-d69a3821dc1a-image.png] I have a DNS record that point's to my WAN IPv4, not my WAN IPv6, so I had to use my IPv6 WAN IP to connect to the GUI. I had a cert warning from my browser, of course. But the access worked well : [image: 1602091959151-63a2eab4-54c2-4efa-9ef7-04825ab0f777-image.png] "Well" means for me : knowing that my IPv6 is using a tunnel to tunnel.ne.net (Huricane IPv6 ISP) the speed was somewhat limited, about 10 Mbytes /sec. I could browse the entire pfSense GUI very well, no hick-ups .... edit : I'll leave the IPv6 access open for a while. PM me, and I can even send you an 'access' so you can test drive yourself. That is, if you promise not to change something, as this is a "live' environment ;)
  • 0 Votes
    7 Posts
    3k Views
    J
    Removing the coax caused pfsense to lose connection, but maintain the DCHP address it had. I was logged in to the gui and could still use it as long as I stayed away from the dashboard. The dashboard did load very slowly but did load after a few minutes. Logging out and then logging back in, where the default starting point is the gui, did not ever load and eventually returned this: [image: 1594594724498-screen-shot-2020-07-12-at-4.51.54-pm.png] I read this is due to widgets, ie the version checking for updates and needing DNS but not having it and eventually timing out. The 8987 bug shows resolved, but did say that the issue is not resolvable at the time. Once I reconnected the coax, everything became stable again and no reboots on the modem or pfsense were needed. That is not what happened to me yesterday, I had to reboot both the modem and pfsense. Is this something I need to live with, not being able to check the status of my WAN via pfSense when my isp goes down? Is there a command line equivalent of this gateway status shown in the dashboard? [image: 1594595191411-screen-shot-2020-07-12-at-5.05.53-pm.png] Thanks, Jerold
  • 0 Votes
    6 Posts
    1k Views
    stephenw10S
    Are the IP addresses you are using both public IPs? What address are you testing from? Something in the same subnet? Can you connect out from the console from the new address? Ping, say, both 8.8.8.8 and google.com? Steve
  • 0 Votes
    8 Posts
    2k Views
    G
    @NogBadTheBad Hi, Sorry i should have mentioned, yeah my PC is on the 10.0.4.X network (just as a test PC) , the aim here was to loose connectivity to the GUI from my PC, then i have another one on the 10.0.7.X range that "should" get access to the GUI. After thinking about this last night I think I have sussed it out, we are going through a Proxy and this is the IP Address that accesses the Management GUI, hopefully I should be able to add some rules in our other proxy to avoid this Firewall bypassing it. Ill let you know if i have any more issues or if i need more help with this. Thanks for your help!