• [Newbie] Setup VLANs - connecting clients to it?

    11
    0 Votes
    11 Posts
    4k Views
    T
    @Jarhead said in [Newbie] Setup VLANs - connecting clients to it?: You have port 4 on the router going to port 1 on the switch, correct? correct @Jarhead said in [Newbie] Setup VLANs - connecting clients to it?: PVID 1 on port 1 is not a problem, that would just carry your untagged traffic on igc3. check @Jarhead said in [Newbie] Setup VLANs - connecting clients to it?: Turn on the DHCP server on all the vlans and then plug in to switchport 5, do you get an address? I don't understand what just happened. I have switched on DHCP for all VLANs and have received a correct IP on the corresponding ports and was also able to call up the interface and reach the gateway via ping. I then switched the DHCP servers off again, manually set IP addresses on all ports again for the client to match the port and tested... Still works. Apart from that, I have not made any other changes. So yes, it works now - so I seem to have understood the principle correctly after all. Shall we blame the switch? :D BIG THANKS TO YOU! You rarely experience such patience with a newbie these days!
  • VLAN not able to get address from Windows DHCP server

    7
    1
    0 Votes
    7 Posts
    4k Views
    N
    @Gazza77 do not include downstream interfaces (WAN) in dhcp-relay
  • Need to setup VLAN with Bridged Mode in pFsense 2.7.2

    13
    0 Votes
    13 Posts
    4k Views
    N
    for doing this task , you'd better buy hardware with multiple network cards for the NUC Mini PC Windows Intel N100, Celeron J6412, HDMI, DP, RS232, COM, RJ45, LAN, PCIE, Wi-Fi, fanless,
  • VPLS like Plan - Ipsec Over OPENVPN-L2 TUNNEL and FRR functionality.

    1
    0 Votes
    1 Posts
    701 Views
    No one has replied
  • SMB | Two Vlans

    10
    0 Votes
    10 Posts
    3k Views
    GertjanG
    @yuriewcli said in SMB | Two Vlans: For the sake of the discussion, i'll say IT dept network range is 10.0.12.0/24. Support Dept is 10.0.11.0/21 where the printer is also connected. Now, the thing is, printing is okay, we can print from IT dept. But we can't scan. First : 10.0.11.0/21 : are you sure about that /21 ? Without firing up my network calculator, this /21 might overlap your 10.0.12.0/24 .... introducing network issues. A device, lets imagine a Windows PC, living on 10.0.12.0/24 can connect to a device on 10.0.11.3/24 (the printer) : it can print. If SMB doesn't seem to work : use the printer IP, and your good. Or assign a local DNS host name to "10.0.11.3" and use that wherever possible. The other way around : the scanner : did you check that the destination of the scanner, as it is a device living outside of the local (printer's point of view) is reachable , Windows devices, afaik, only accept, by default SMB traffic from their own local network, like 10.0.12.0/24 only. You have to visit the Windows firewall on that PC, and add other networks like 10.0.11.0/24. Normally, you should have a shared directory on the PC so the scanner can access it and drop the image or PDF scanned files.
  • 2.5Gb port reading as 1Gb on Protectli Vault

    1
    0 Votes
    1 Posts
    575 Views
    No one has replied
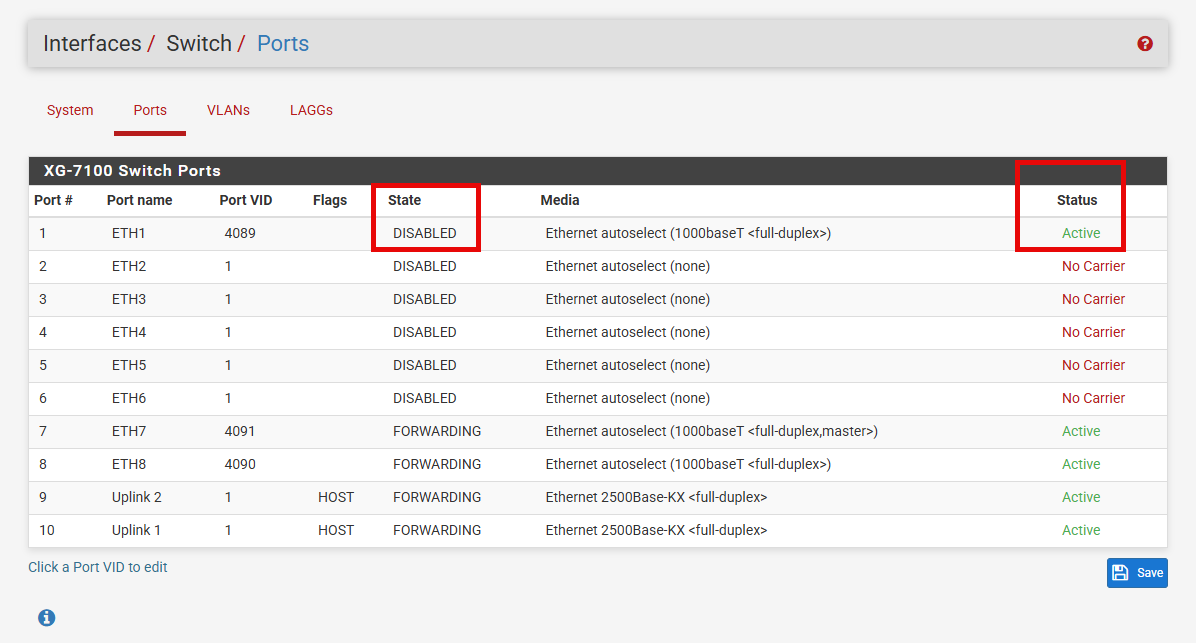
  • Interface showing as DISABLED

    2
    3
    0 Votes
    2 Posts
    984 Views
    stephenw10S
    What do you see in the output of etherswitchcfg at the CLI?
  • Routing traffic without involving the firewall and/or interfaces !! :)

    1
    0 Votes
    1 Posts
    555 Views
    No one has replied
  • Creating vlan and testing via direct Windows PC connection

    11
    6
    0 Votes
    11 Posts
    3k Views
    K
    @patient0 - I have larger problems (which I can handle). The SSD in the 5100 has crapped out. It started with lots of odd errors, which this appears to be one of. But config files started having errors. And then the 5100 would not boot. I have ordered a new SSD and will recover from there. Thanks for the help! You had me in the right direction!!
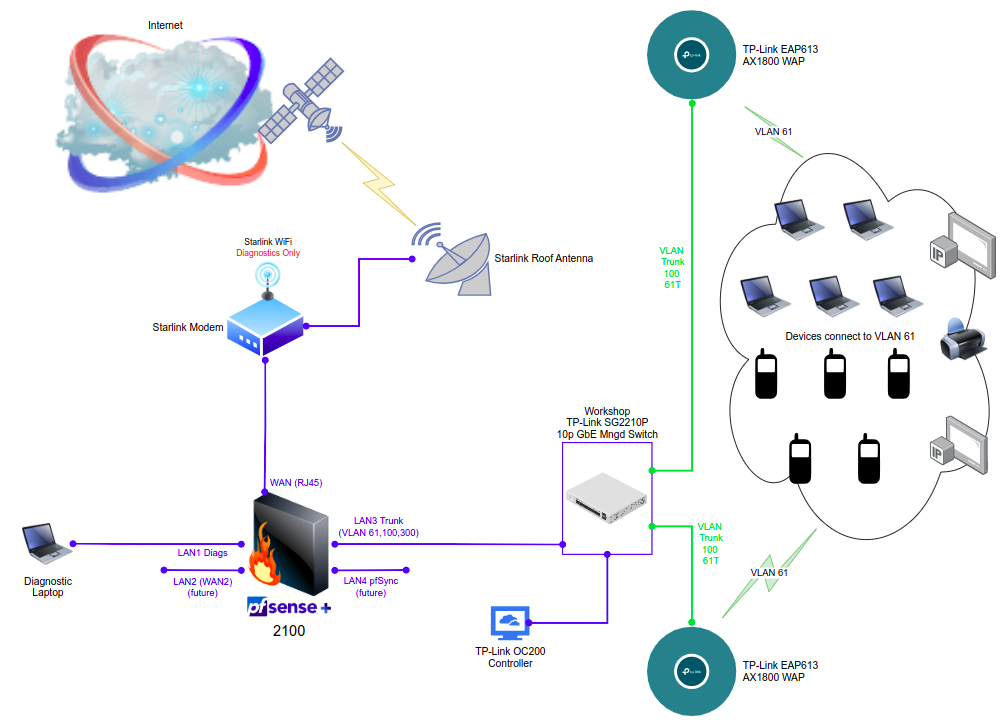
  • 2100 - Adding 3 VLAN's to LAN3 Port question

    4
    4
    0 Votes
    4 Posts
    1k Views
    J
    Found the problem. I'd forgotten to enable the DHCP service on Office VLAN 61. The below is the correct configuration for adding multiple VLAN tags to a discrete interface [image: 1741759623930-screenshot-from-2025-03-12-10-22-04.png] Additional Information can be found on YouTube Link Here Jim Pingle Configuring Netgate Appliances Integrated Switches on pfSense 2.4.4. July 2018 Hangout (thank you Jim and @patient0 )
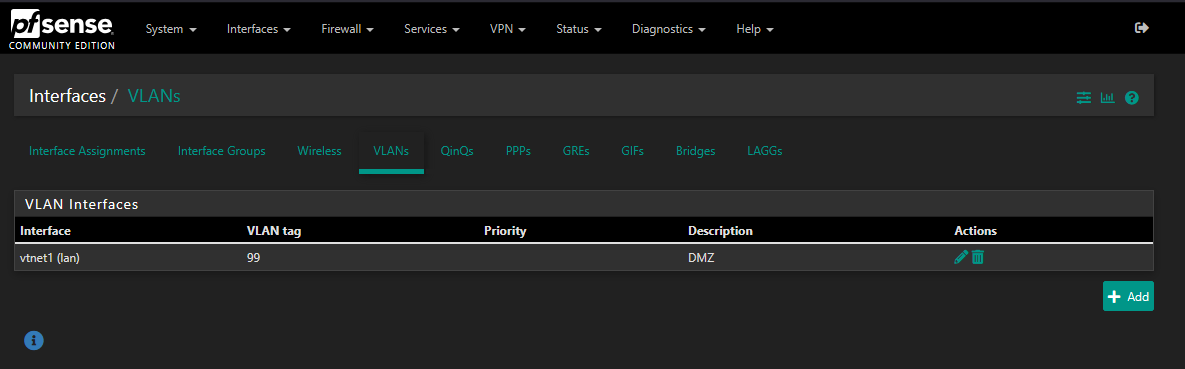
  • Cannot get VLAN to work in any way

    6
    6
    0 Votes
    6 Posts
    1k Views
    K
    @viragomann I replied above but it might not have updated for you if you were typing. I enabled vlan awareness but didnt know i had to restart my proxmox host for it to work. I now am able to get IPs in the .99 subnet range
  • Speed negotiation with LAN Bridge

    1
    2
    0 Votes
    1 Posts
    360 Views
    No one has replied
  • Why can my VLAN ping other devices on different subnet?

    7
    6
    0 Votes
    7 Posts
    2k Views
    R
    @Bob-Dig Thanks Bob. The extra rules explained in the video did the trick.
  • 6100 failover LAG - slow bandwidth

    1
    0 Votes
    1 Posts
    510 Views
    No one has replied
  • Mac-based Vlan Authetification

    4
    0 Votes
    4 Posts
    1k Views
    M
    @dominikmorawietz Sounds like you want SDA or something with similar functionality. I don't think the functionality you're looking for is done at the firewall level. You'll likely need to implement something internally before it hits the firewall.
  • Mixed MTUs on different NIC's interfaces on same pfSense bare metal

    9
    0 Votes
    9 Posts
    3k Views
    JKnottJ
    @Sergei_Shablovsky said in Mixed MTUs on different NIC's interfaces on same pfSense bare metal: How different MTUs on physically different interfaces (if NIC are 2- or 4- head model) impact on NIC's overall performance (overall throughput, numbers of IRQs, etc...) ? As mentioned before, there is no effect between different NICs. The only issue is there will be more work with smaller packets on the computer/switch/router. This is because those devices handle Ethernet frames as a whole. So, the smaller the MTU, the more frames that have to be handled and the more work for the CPU in those devices.
  • Another vlan w/o network access issue

    vlan internet access
    15
    8
    0 Votes
    15 Posts
    4k Views
    G
    @algo7 said in Another vlan w/o network access issue: It's always Netgear. Their VLAN configuration is always a PITA. Ran into almost the exact issue today. What issue? There was nothing wrong with Netgear, just the port assignments...
  • Beginner - N2000 how to set port 4 to it's own network?

    7
    0 Votes
    7 Posts
    1k Views
    B
    @patient0 said in Beginner - N2000 how to set port 4 to it's own network?: That's very odd, it's a valid range and does have to work. If both the LAN1 and OPT1 are set to /24 they are not overlapping. And if neither the WAN nor the network being your parents AP are using the same IP range, then it should work. I agree that it's odd and now that it's working I'm hesitant to mess with it again. I guess I could always backup my configuration, break it and then put it back to what I know works.
  • PERDIDA DE CONECTIVIDAD

    2
    0 Votes
    2 Posts
    477 Views
    patient0P
    @cesarin En esta parte del foro el idioma es el inglés. Hay una parte en español de este foro: https://forum.netgate.com/category/11/espa%C3%B1ol. O puedes escribir en inglés si eres capaz. If you like to go on in English: What is the pfSense version that is in use and what is the device you run pfSense on? Is the pfSense device connected to a network switch? From your description: there is a network named "LAN" on network interface igb1 (192.168.150.10/24) and a network named VOIP on VLAN 155 with parent interface igb1 (192.168.155.1/24). And you have to restart the VOIP interface to make it work again? How long does it work before you have to restart the interface?
  • Best practice for entertainment devices

    4
    0 Votes
    4 Posts
    943 Views
    S
    @NGUSER6947 TL DR - Don't use VLANs when a firewall alias is the more appropriate solution. You don't want to get too granular with your VLANs IMHO. I think most home networks only need 3 VLANs. 1 - a "Secure" VLAN for the router/firewall device itself and other network equipment, as well as all of your personal data. This likely includes most of your personal computers/laptops, network storage devices, etc, but it does NOT include personal mobile devices like phones and tablets. Devices on this VLAN should be able to access any other VLAN. 2 - a "No Internet" VLAN for any device that doesn't need internet access. This might include a lot of the automation devices in your network, CCTV cameras, any network printers, etc etc. Of course the VLAN not having internet doesn't mean you won't be able to access these devices either locally or remotely (over a VPN connection), because you will still be able to do that if setup that way. Devices on this VLAN shouldn't have access to any other VLAN. 3 - an "Everything else" VLAN for........ you guessed it......... everything else (ie your media servers, smart TVs, mobile devices, etc.) Basically anything that needs an internet connection but isn't "secure" enough, or has no reason to be accessing your personal data (which resides on the "Secure" VLAN) needs to go on this VLAN. Not only do your personal mobile devices need to be on this VLAN for security reasons, it's also easier to cast/stream to the media servers when everything is on the same VLAN. Honestly the vast majority of your devices will likely fall onto this VLAN. Devices on this VLAN would have access to the "No Internet" VLAN only. When you have just a small number of devices that you want to handle differently, this is when you can/should create firewall "aliases" and control groups of devices this way. Most of the time an alias is a better way to manage the devices than a full blown VLAN IMHO. So no, I would not create an "Entertainment VLAN" because that is getting too granular with your VLANs, but I probably would create an "entertainment" firewall alias if I wanted to handle those devices differently when it comes to ad blocking, rules, or other typical firewall activities. PS - I know a lot of people want to have a "Guest" wireless network/vlan but that isn't actually needed most of the time now that your guests are generally going to have a mobile phone and mobile internet service that works well. Perhaps if your home is located in a cellular "dead spot" this would be helpful to your guests, otherwise it really isn't needed. I know that I initially created a guest network and it was only used perhaps twice over about a 5 year period, so I eventually did away with it. Having a guest network that isn't actually used/needed is nothing but a security risk that should be eliminated.
Copyright 2026 Rubicon Communications LLC (Netgate). All rights reserved.
Privacy Policy · Cookie Policy